Shift left without the false-positive tax
AppSec, cloud and supply-chain security wired into the pipeline — ranked by what is actually reachable.
Engineering teams want security that fits the pipeline, not a wall of findings. Connect your SCM, scan every repo with five engines, and let call-graph reachability cut the noise to the ~30% an attacker can reach — then keep it green with CI gates and a shift-left CLI.
01 · What changes
Five scanners, one connect
SAST, SCA, secrets, IaC and DAST from engines we run in-house.
Reachability ranking
Fix the exploitable minority; bulk-suppress dead-code noise.
Cloud + supply chain
IaC, container and CSPM findings in the same model as code.
CI/CD + shift-left CLI
Pre-commit and pipeline checks that report straight back to the platform.
02 · In the product
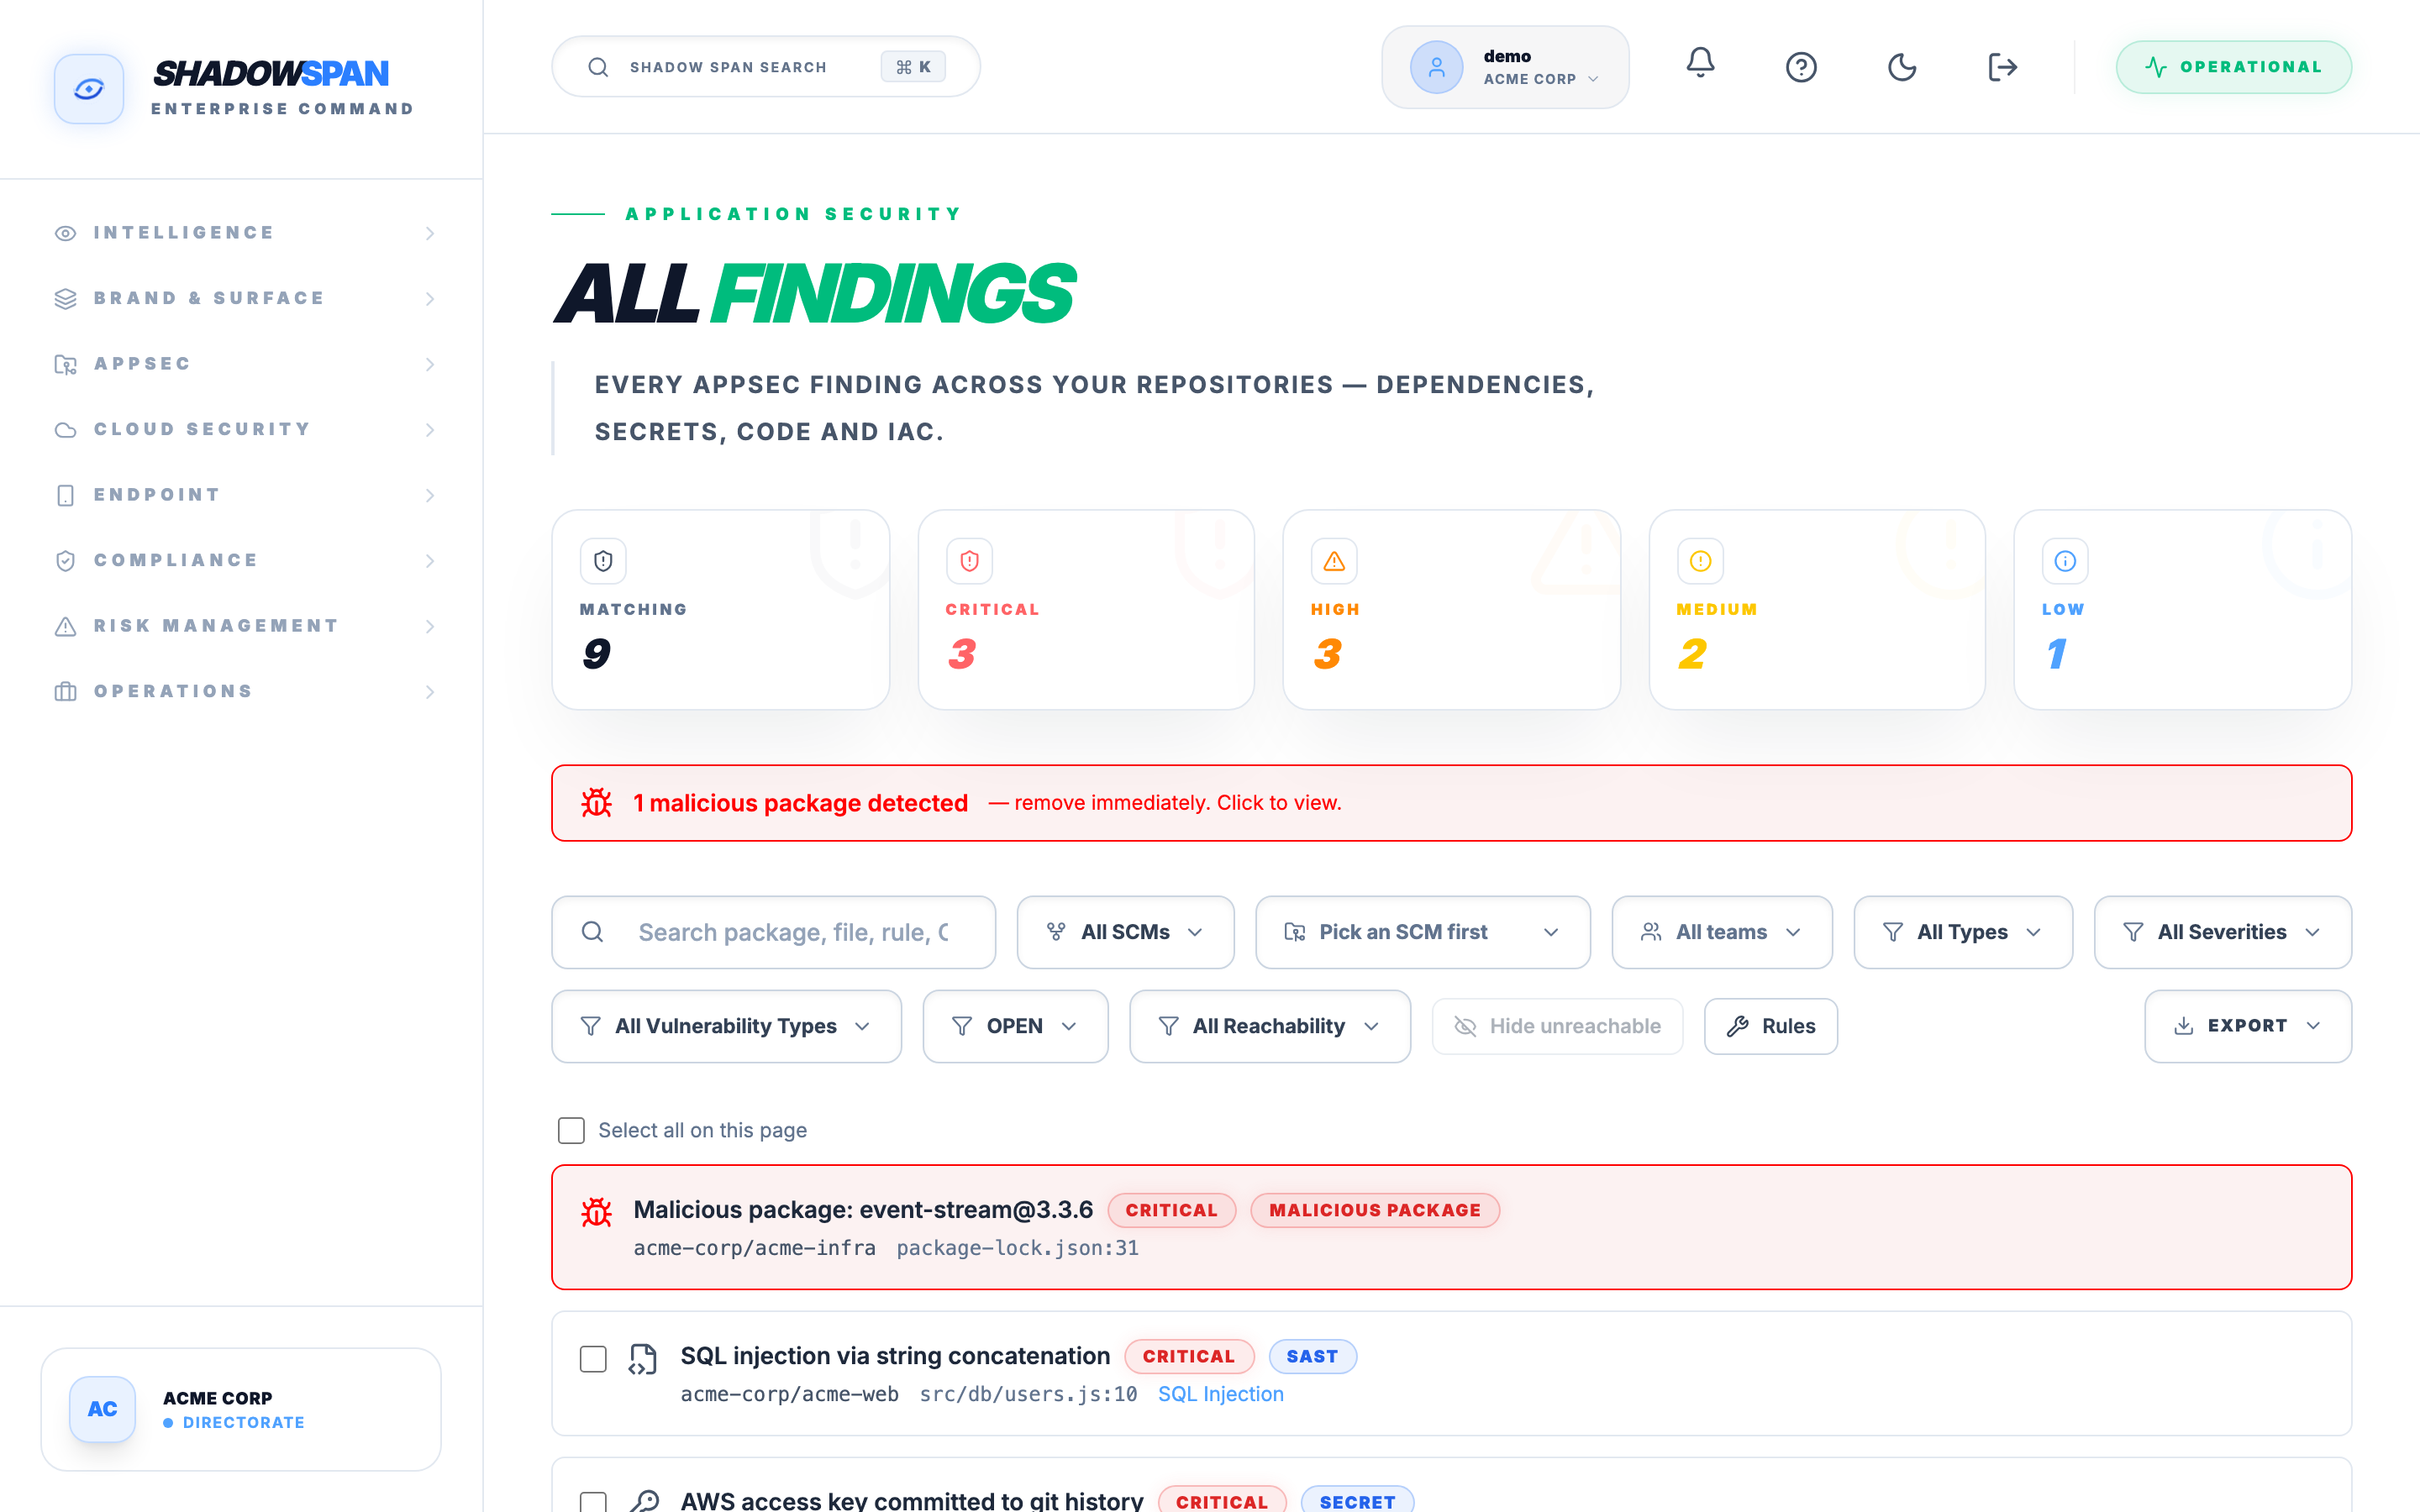
Fig. 01 — Application security
Five scanners, one ranked list
SAST across nine languages, dependency CVEs, leaked secrets, IaC misconfigs and malicious packages — all from a single SCM connect. Malware is flagged CRITICAL and floated to the top; the dead-code rest is one bulk-suppress away.
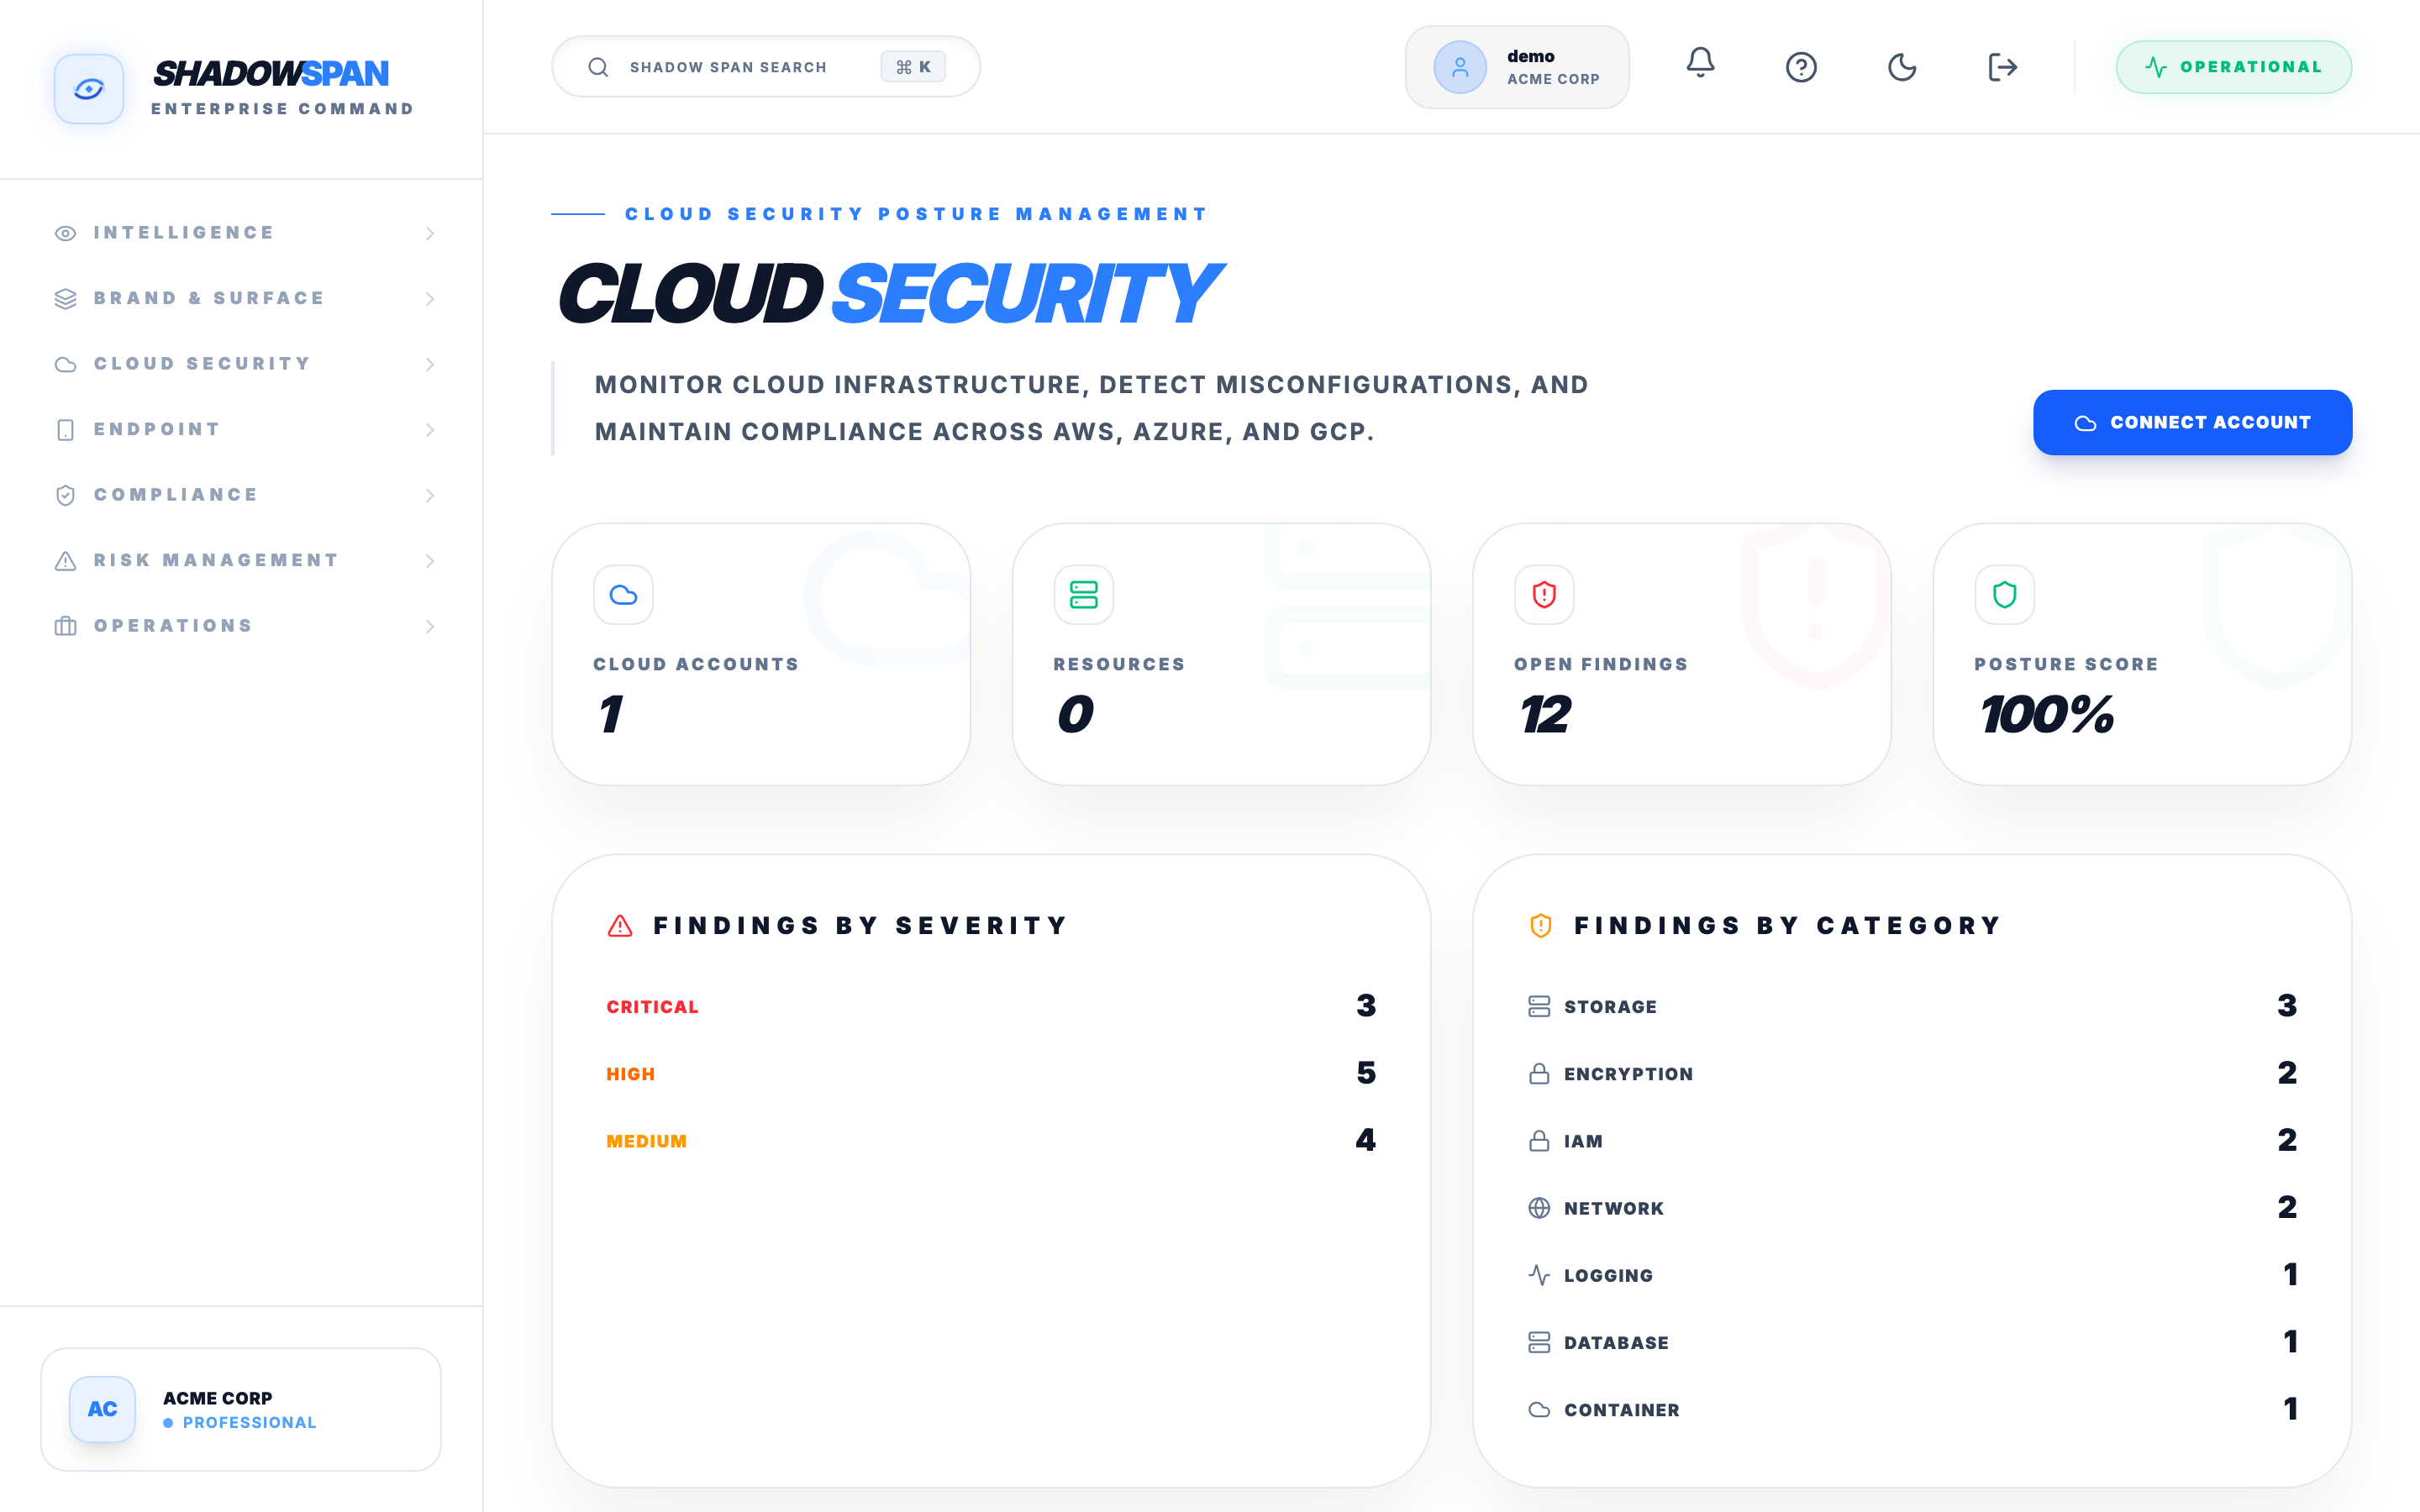
Fig. 02 — Cloud posture
Misconfigs with blast radius
1,000+ CSPM checks across GCP, AWS and Azure, scored by severity and category — then chained into the same attack-path graph as your code, so a public bucket that leads to a privileged role reads differently from one that does not.
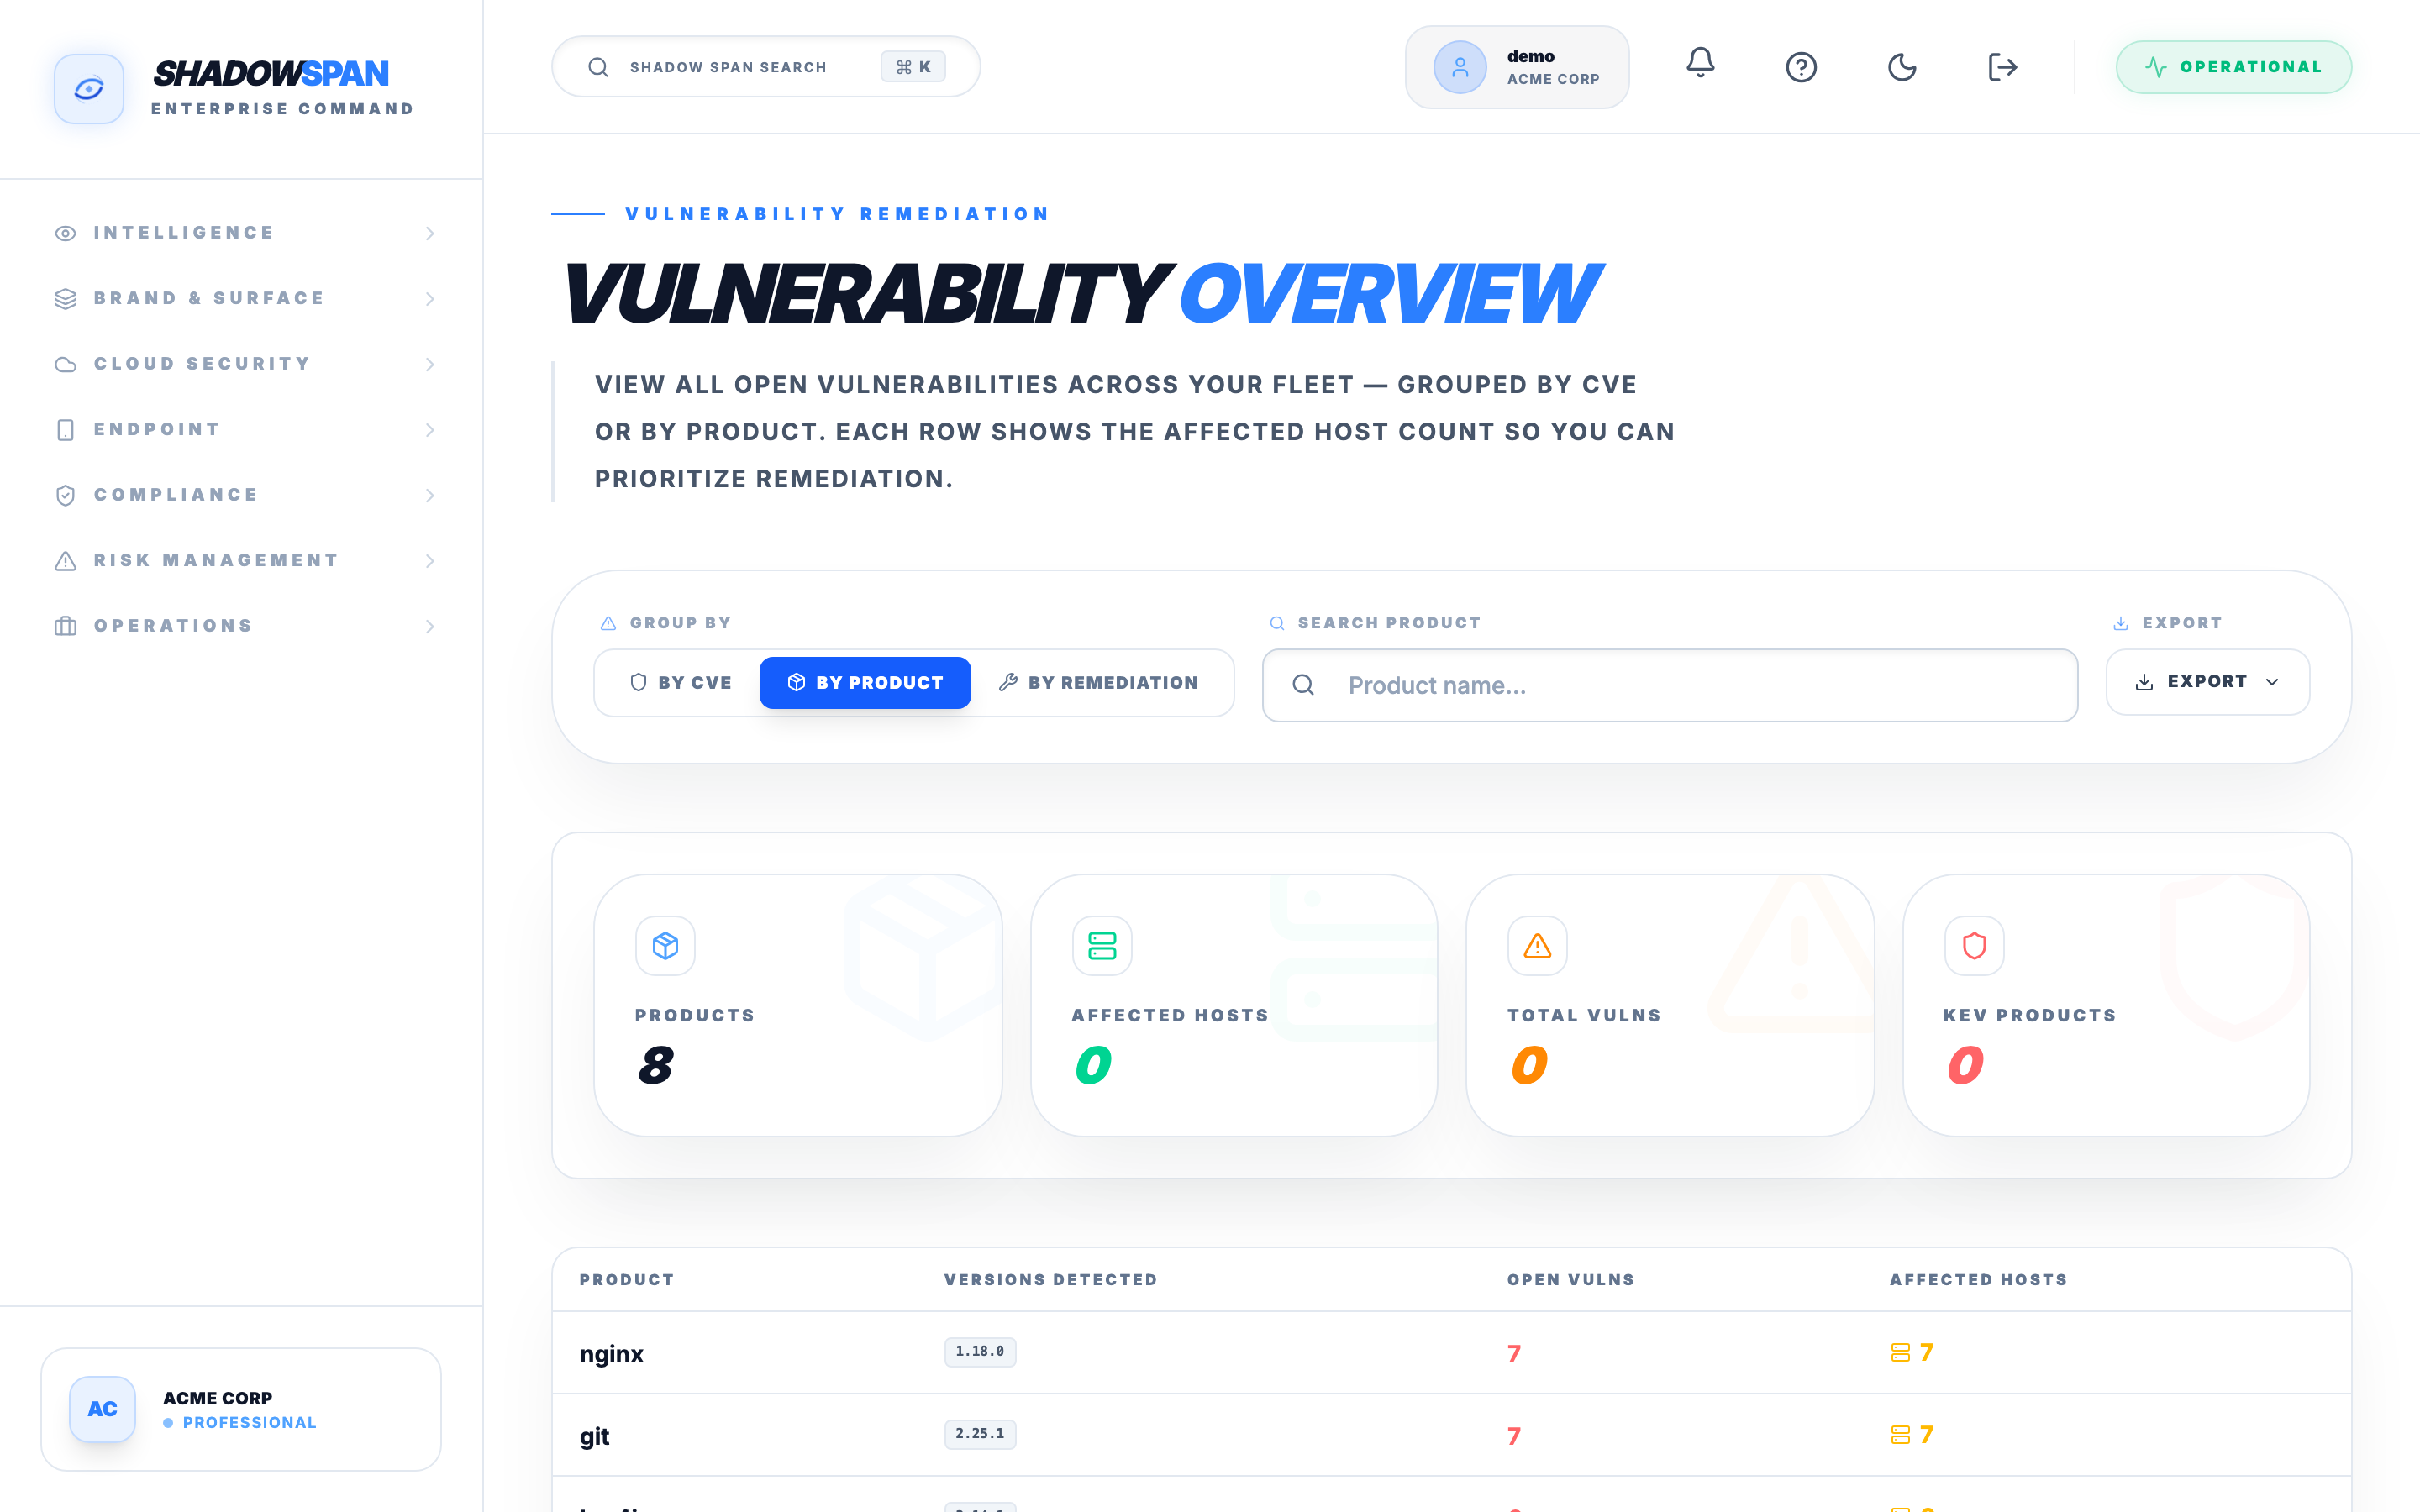
Fig. 03 — Vulnerability & patch
Every open CVE, grouped to act on
Endpoint, cloud and asset vulnerabilities unified and grouped by product, with affected-host counts so you patch the upgrade that closes the most exposure first — not one CVE ticket at a time.
One platform underneath
Every one is part of the same platform — share the data, not the integration tax.
Replace ten tools.
One invoice.
Stop paying up to $350K a year across fragmented point solutions. Get unified visibility, cross-module correlation and AI-powered insights from a single platform.