Compliance proven by your security
Continuous control coverage across 11 frameworks — and the live evidence that proves it.
Compliance is a once-a-year fire drill of screenshots and spreadsheets, disconnected from the security evidence that should prove it.
Continuous control evaluation across 11 frameworks, a risk register with treatment workflows, and evidence auto-collected from your live security data and Drive/Confluence.
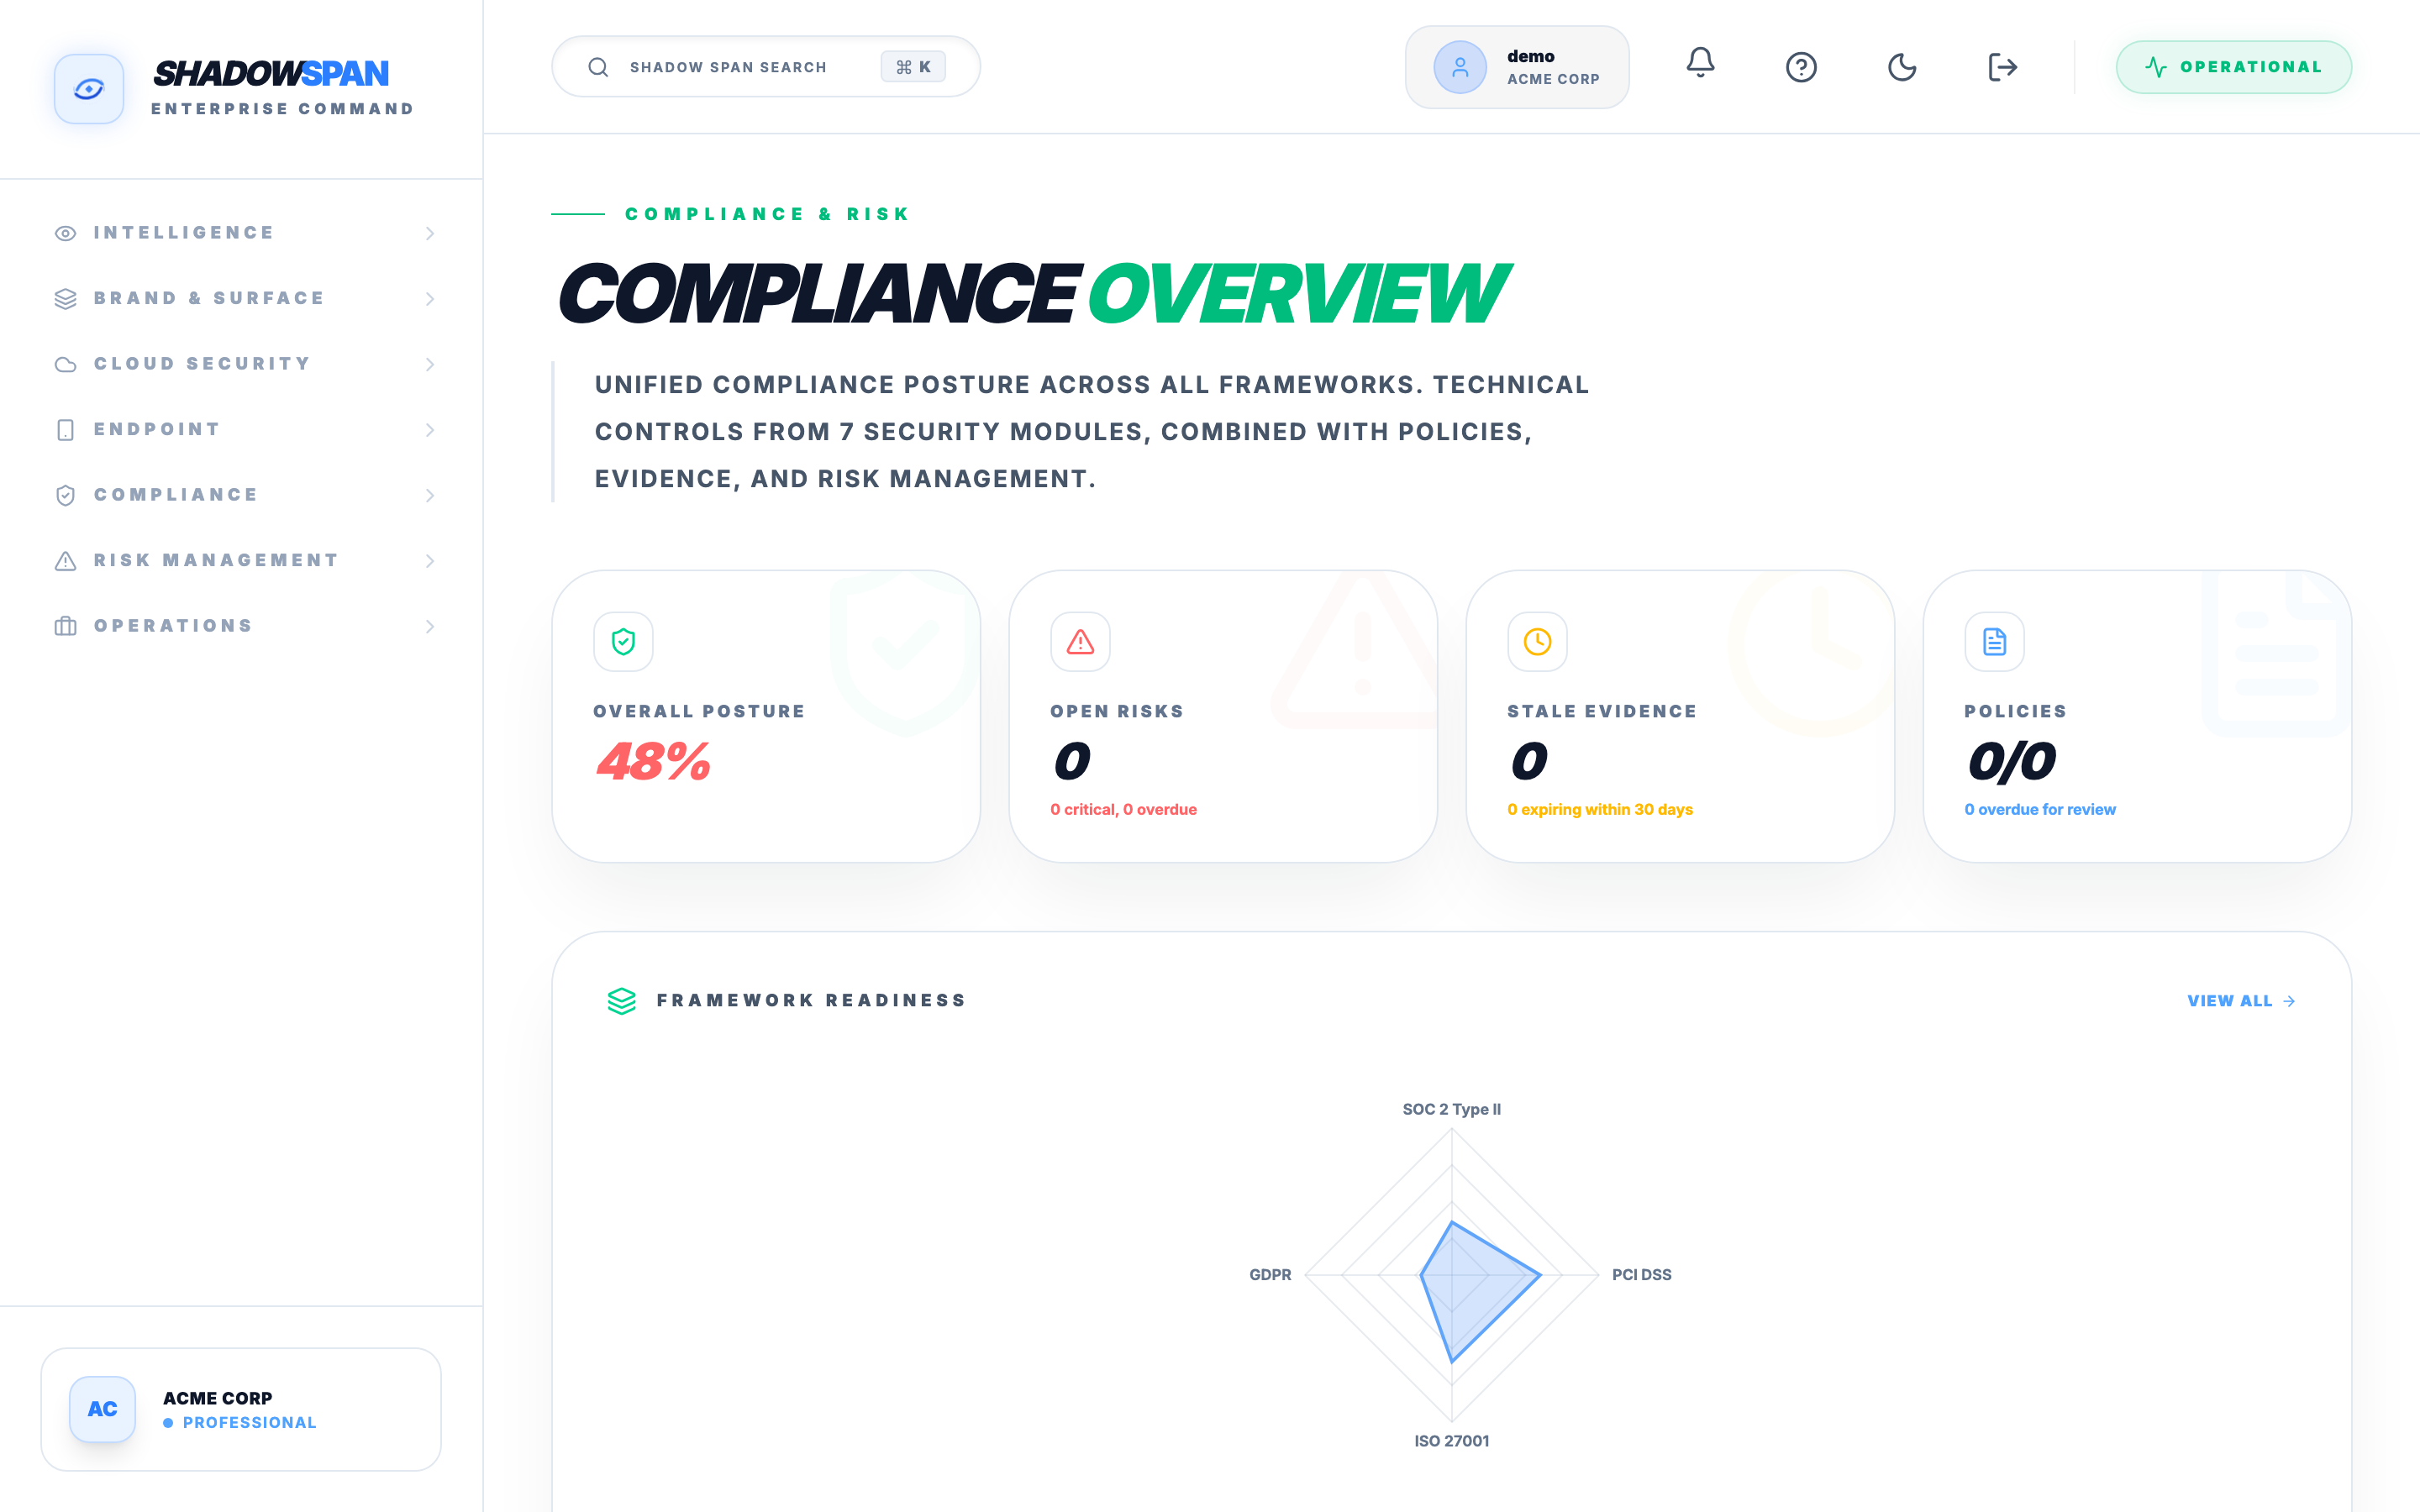
Fig. 01 — Posture + framework readiness across 11 frameworks
01 · In the product
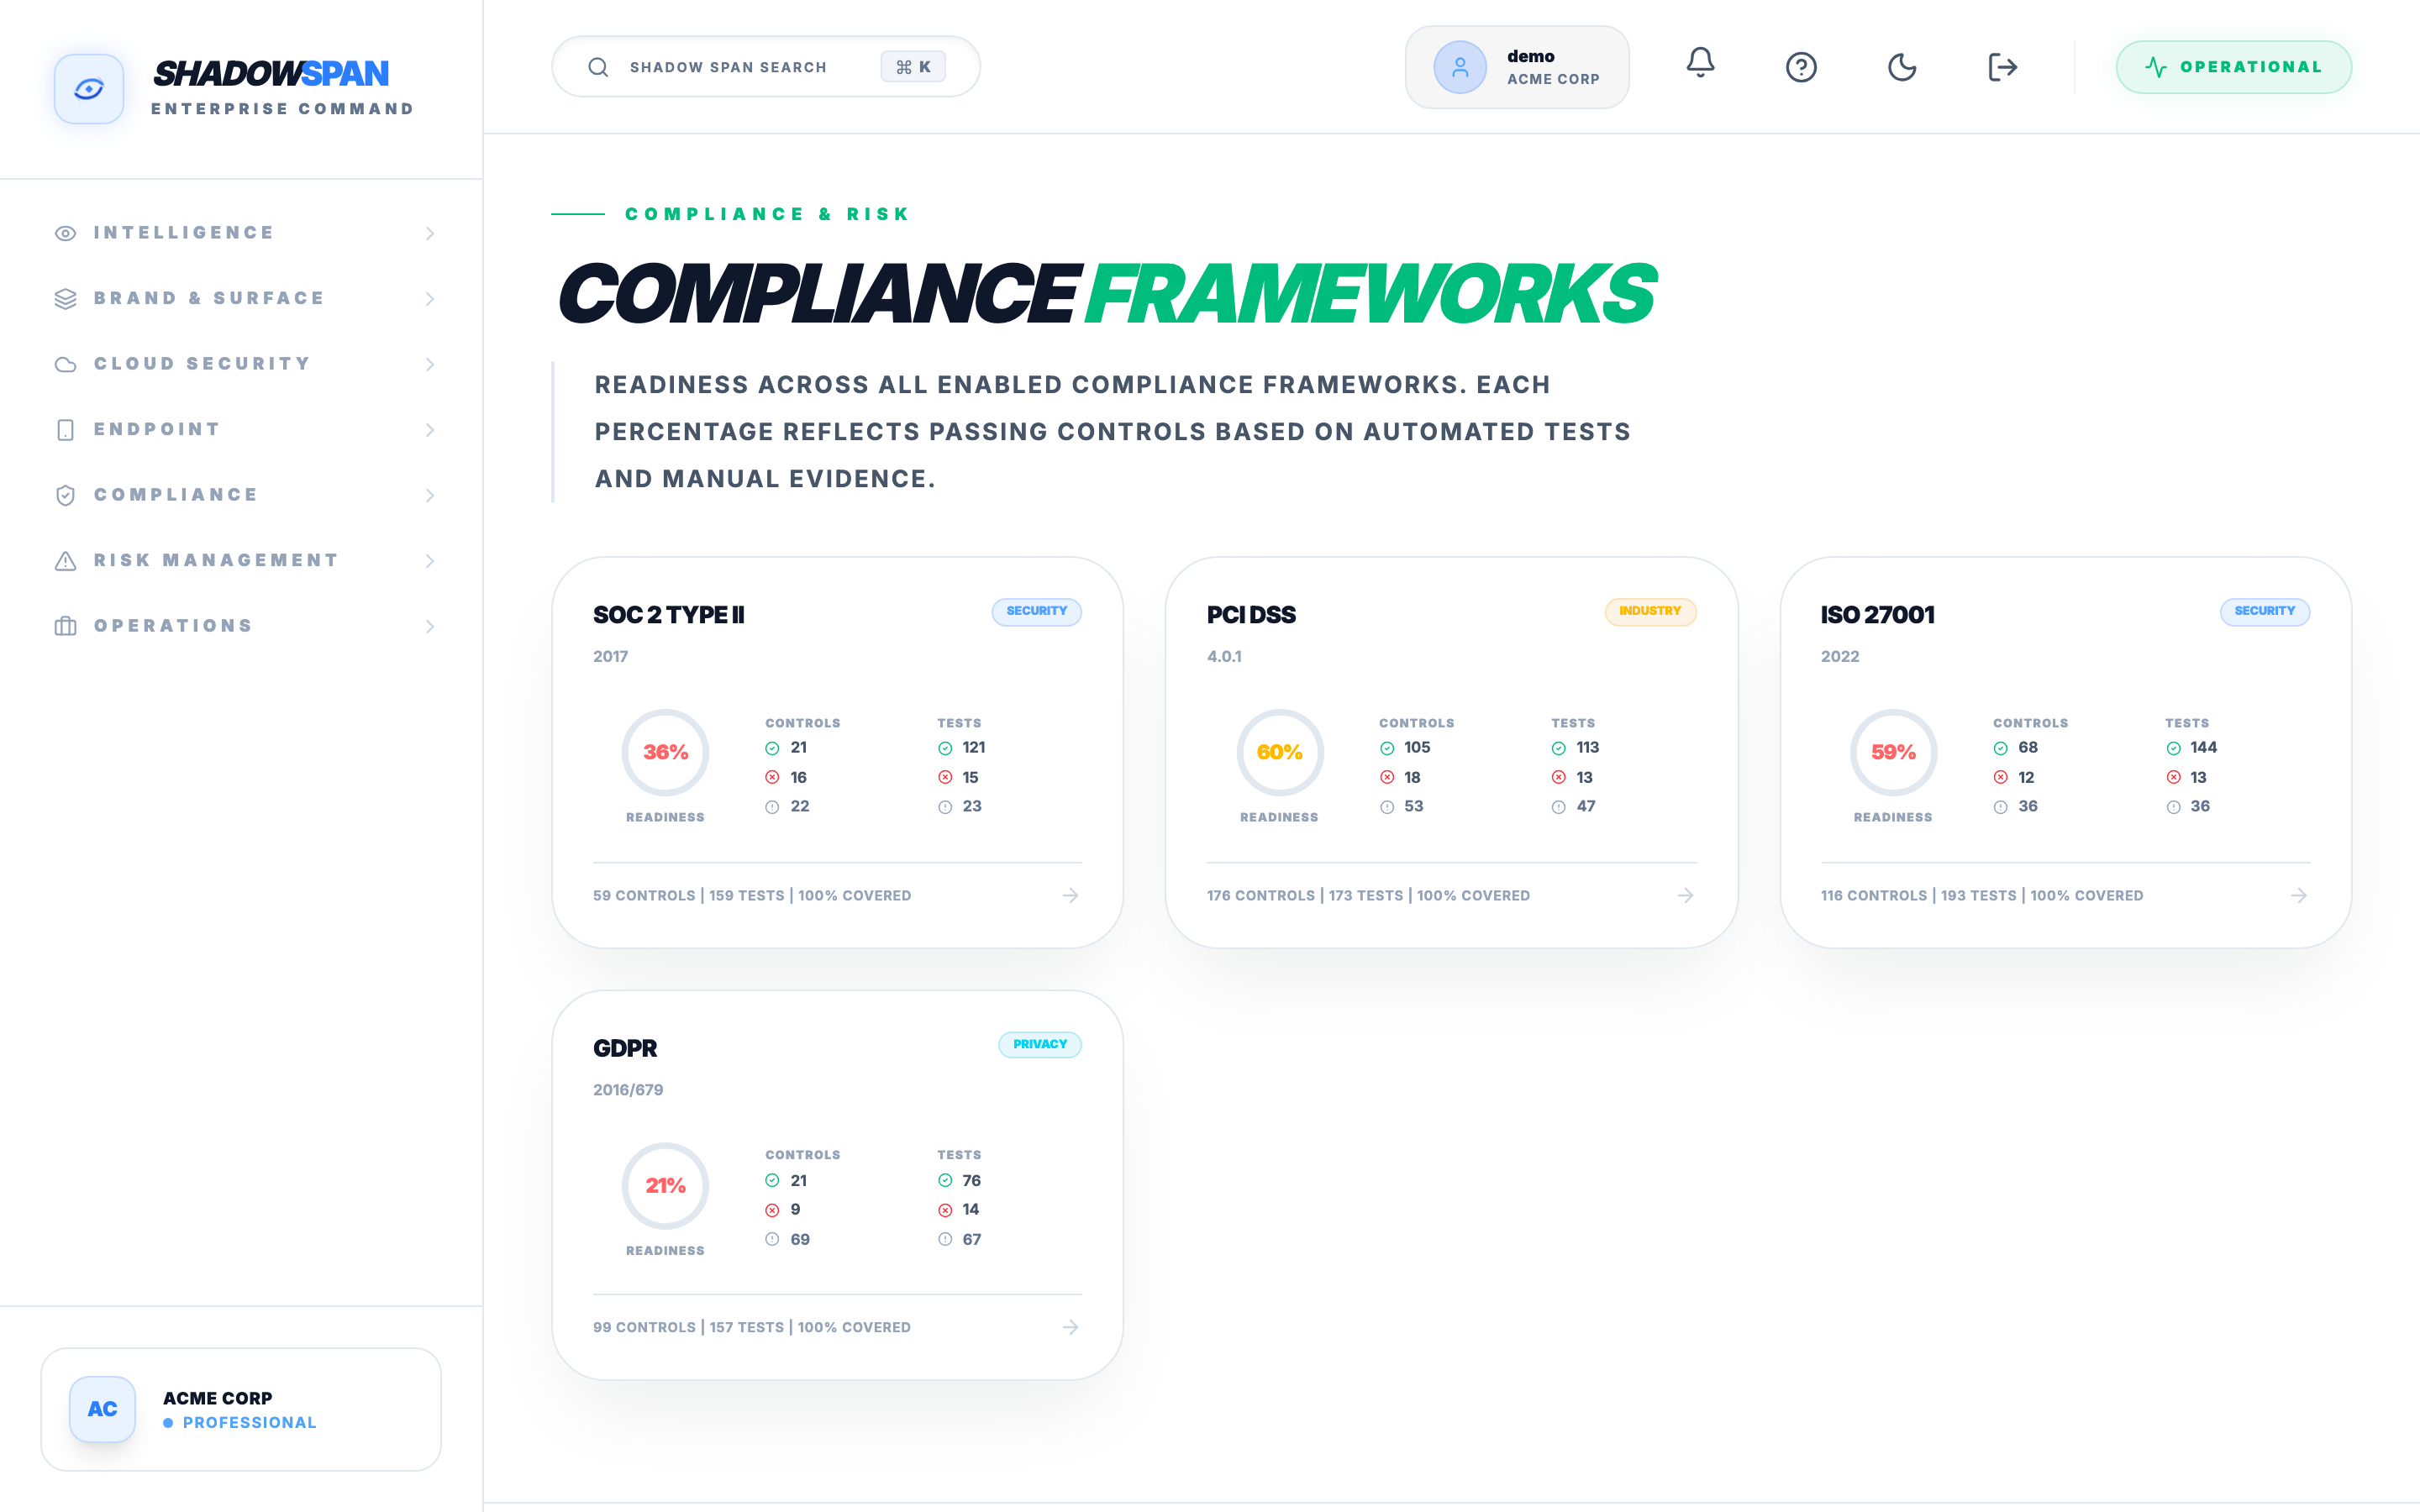
Fig. 02 — Framework readiness
Every framework, one readiness view
Live percentage readiness across all enabled frameworks — SOC 2, PCI DSS, ISO 27001, GDPR and more — each ring driven by passing controls from automated tests and manual evidence, with control and test counts per framework.
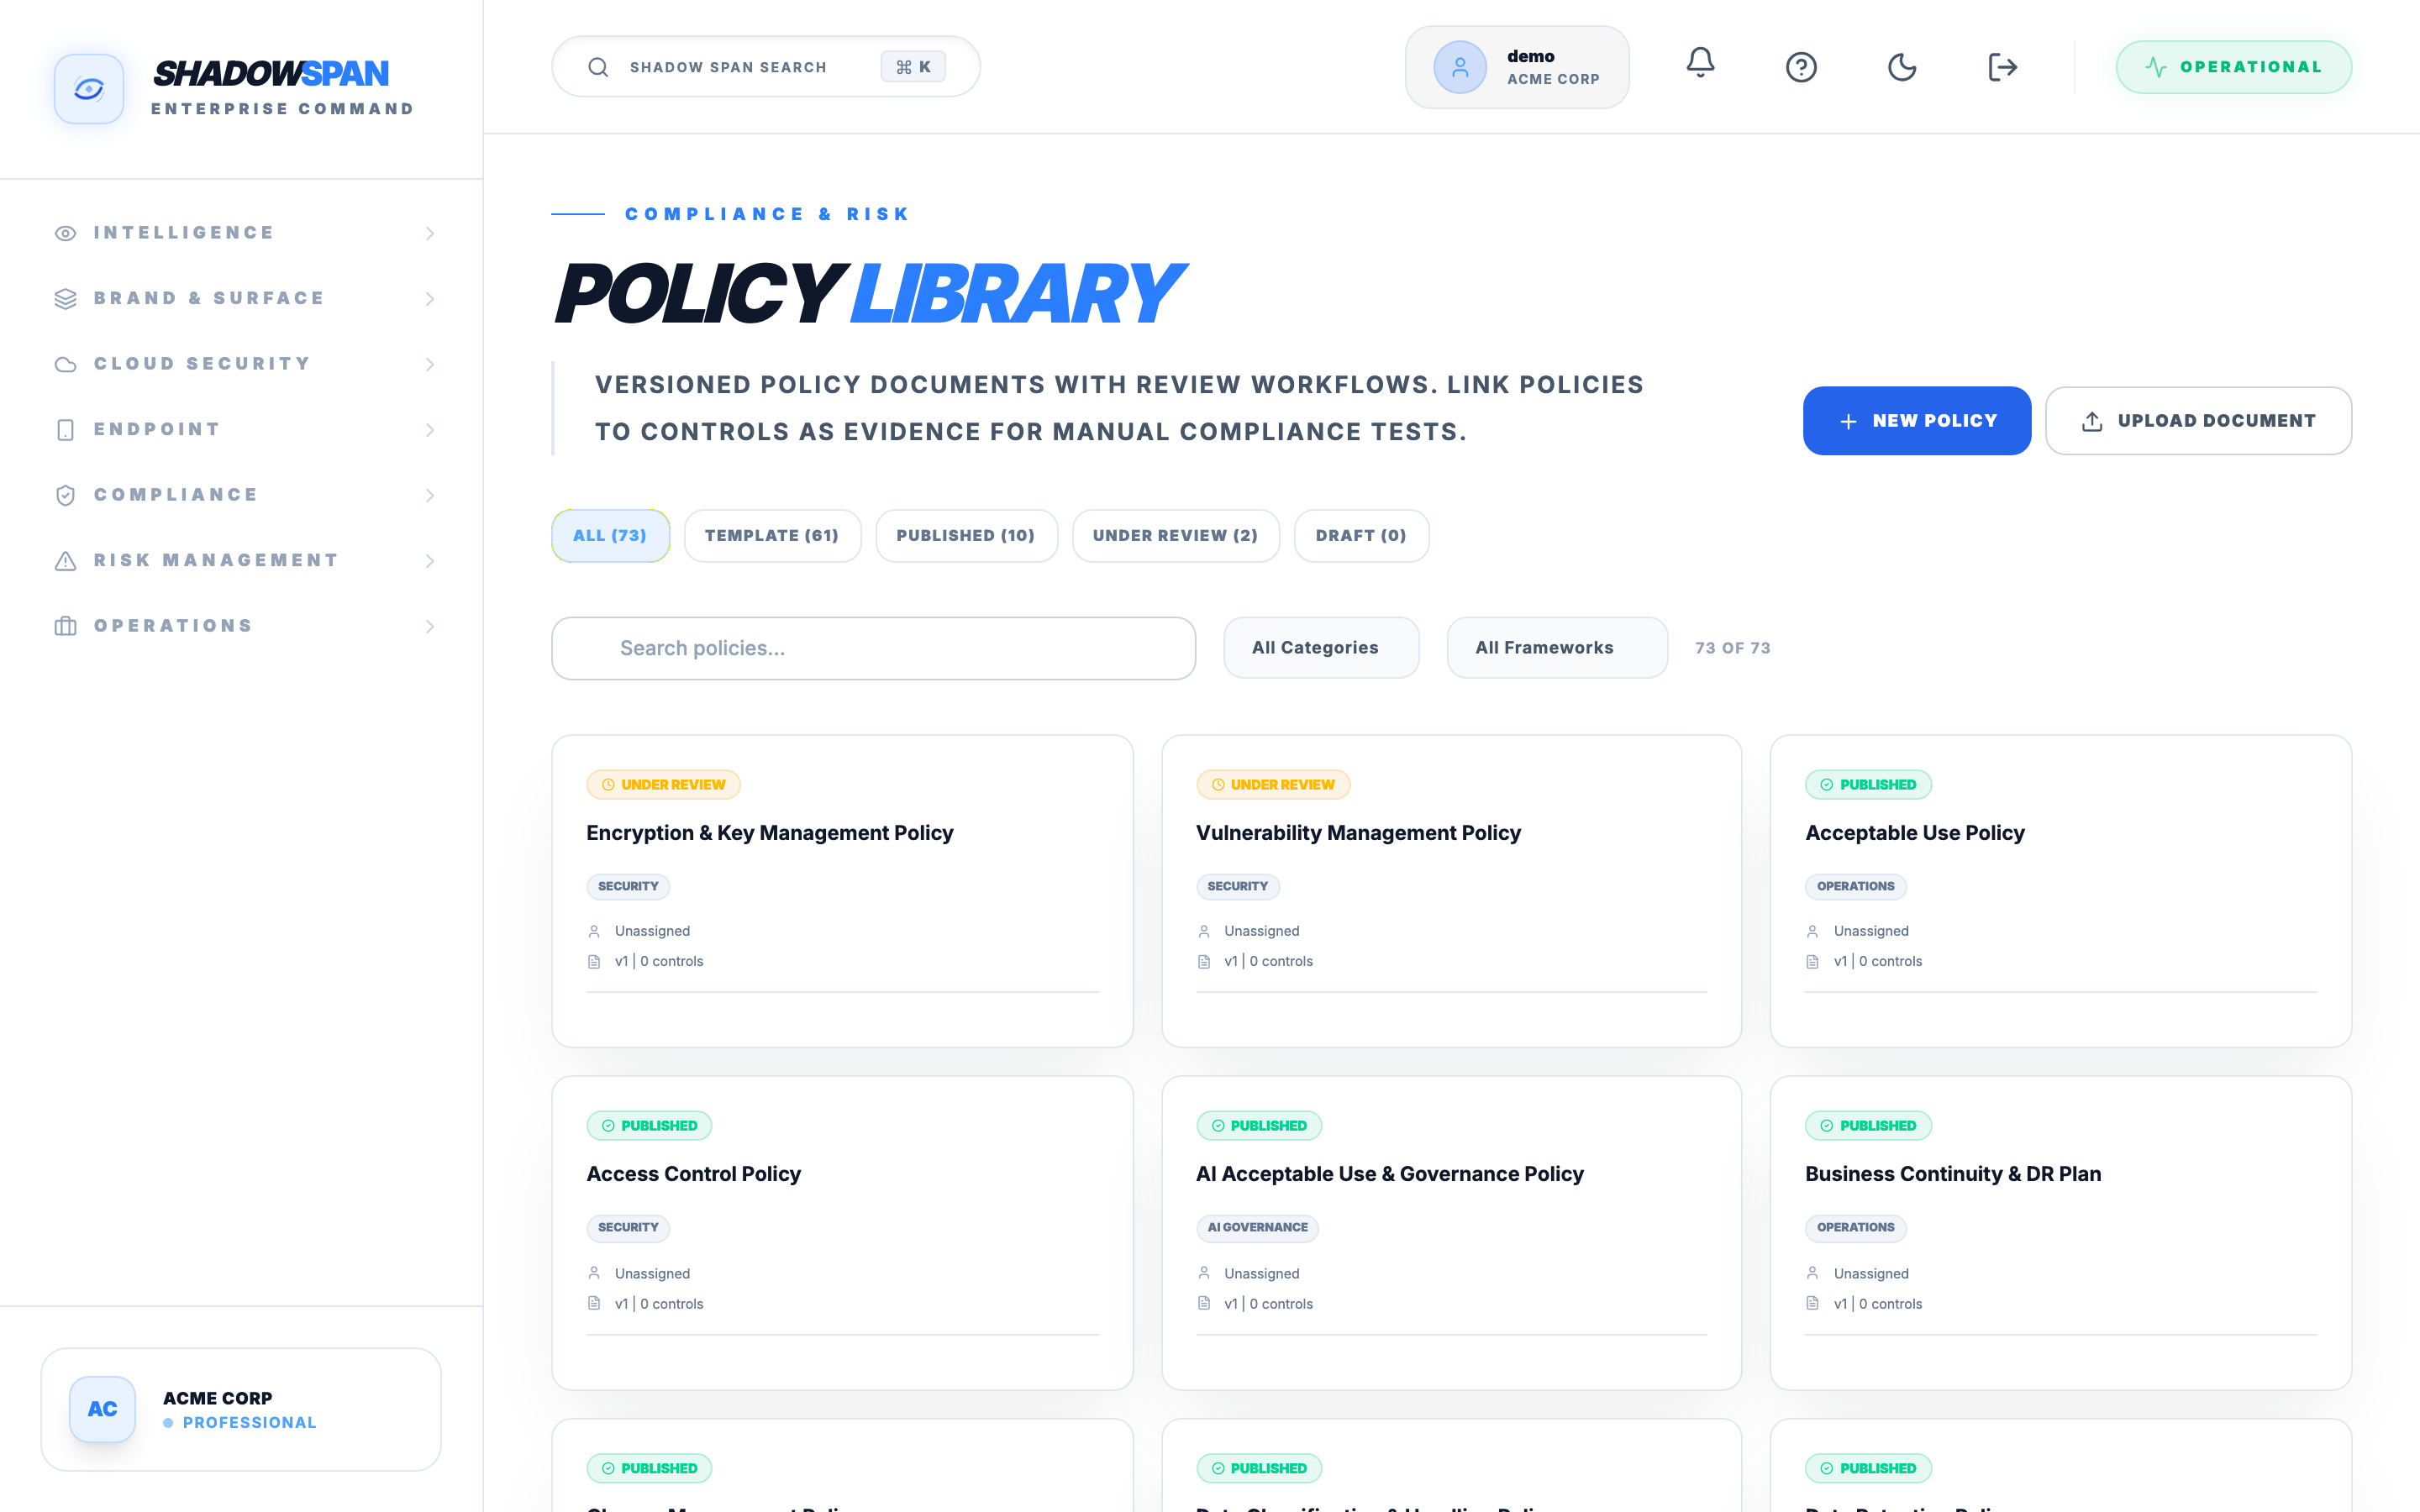
Fig. 03 — Policy library
Policies as evidence, not attachments
Versioned policy documents with review workflows, synced from Google Drive and Confluence and linked to the controls they satisfy — so the policy and the control it backs live together, ready for an assessor.
02 · What you get
11 frameworks
SOC 2, ISO 27001, PCI DSS, NIST CSF, GDPR, DORA, NIS2 and AI frameworks.
Continuous coverage
Evidence pulled from live findings, not annual screenshots.
Risk register (ERM)
Scenario catalog, treatment workflows and mitigating-control mapping.
Cross-framework mapping
Satisfy one control, see every framework it covers.
Policy + document sync
Google Drive and Confluence ingestion into living policy records.
Audit-ready exports
Immutable audit log and executive PDF for assessors.
03 · How it works
Pick frameworks
Select the standards you are held to.
Map to live evidence
Controls bind to your real CSPM, AppSec and vuln data.
Track risk
Risk register with treatment decisions and expiry.
Export
Auditor-ready evidence and reports on demand.
Vanta does compliance. Shadow Span does compliance AND the security that proves it — your CSPM, AppSec, vuln and vendor data ARE the evidence, in one platform.
Works with
Replace ten tools.
One invoice.
Stop paying up to $350K a year across fragmented point solutions. Get unified visibility, cross-module correlation and AI-powered insights from a single platform.