Signal, not firehose
40+ live sources, deduplicated and prioritized — so you act on the 1% that is actually trending.
Threat feeds are firehoses of CVEs and IOCs with no prioritization, and analysts burn out triaging noise.
We aggregate 40+ public advisory, exploit, IOC and breach sources ourselves, then layer Smart Score, EPSS exploit prediction, trending velocity and confidence decay — with natural-language querying.
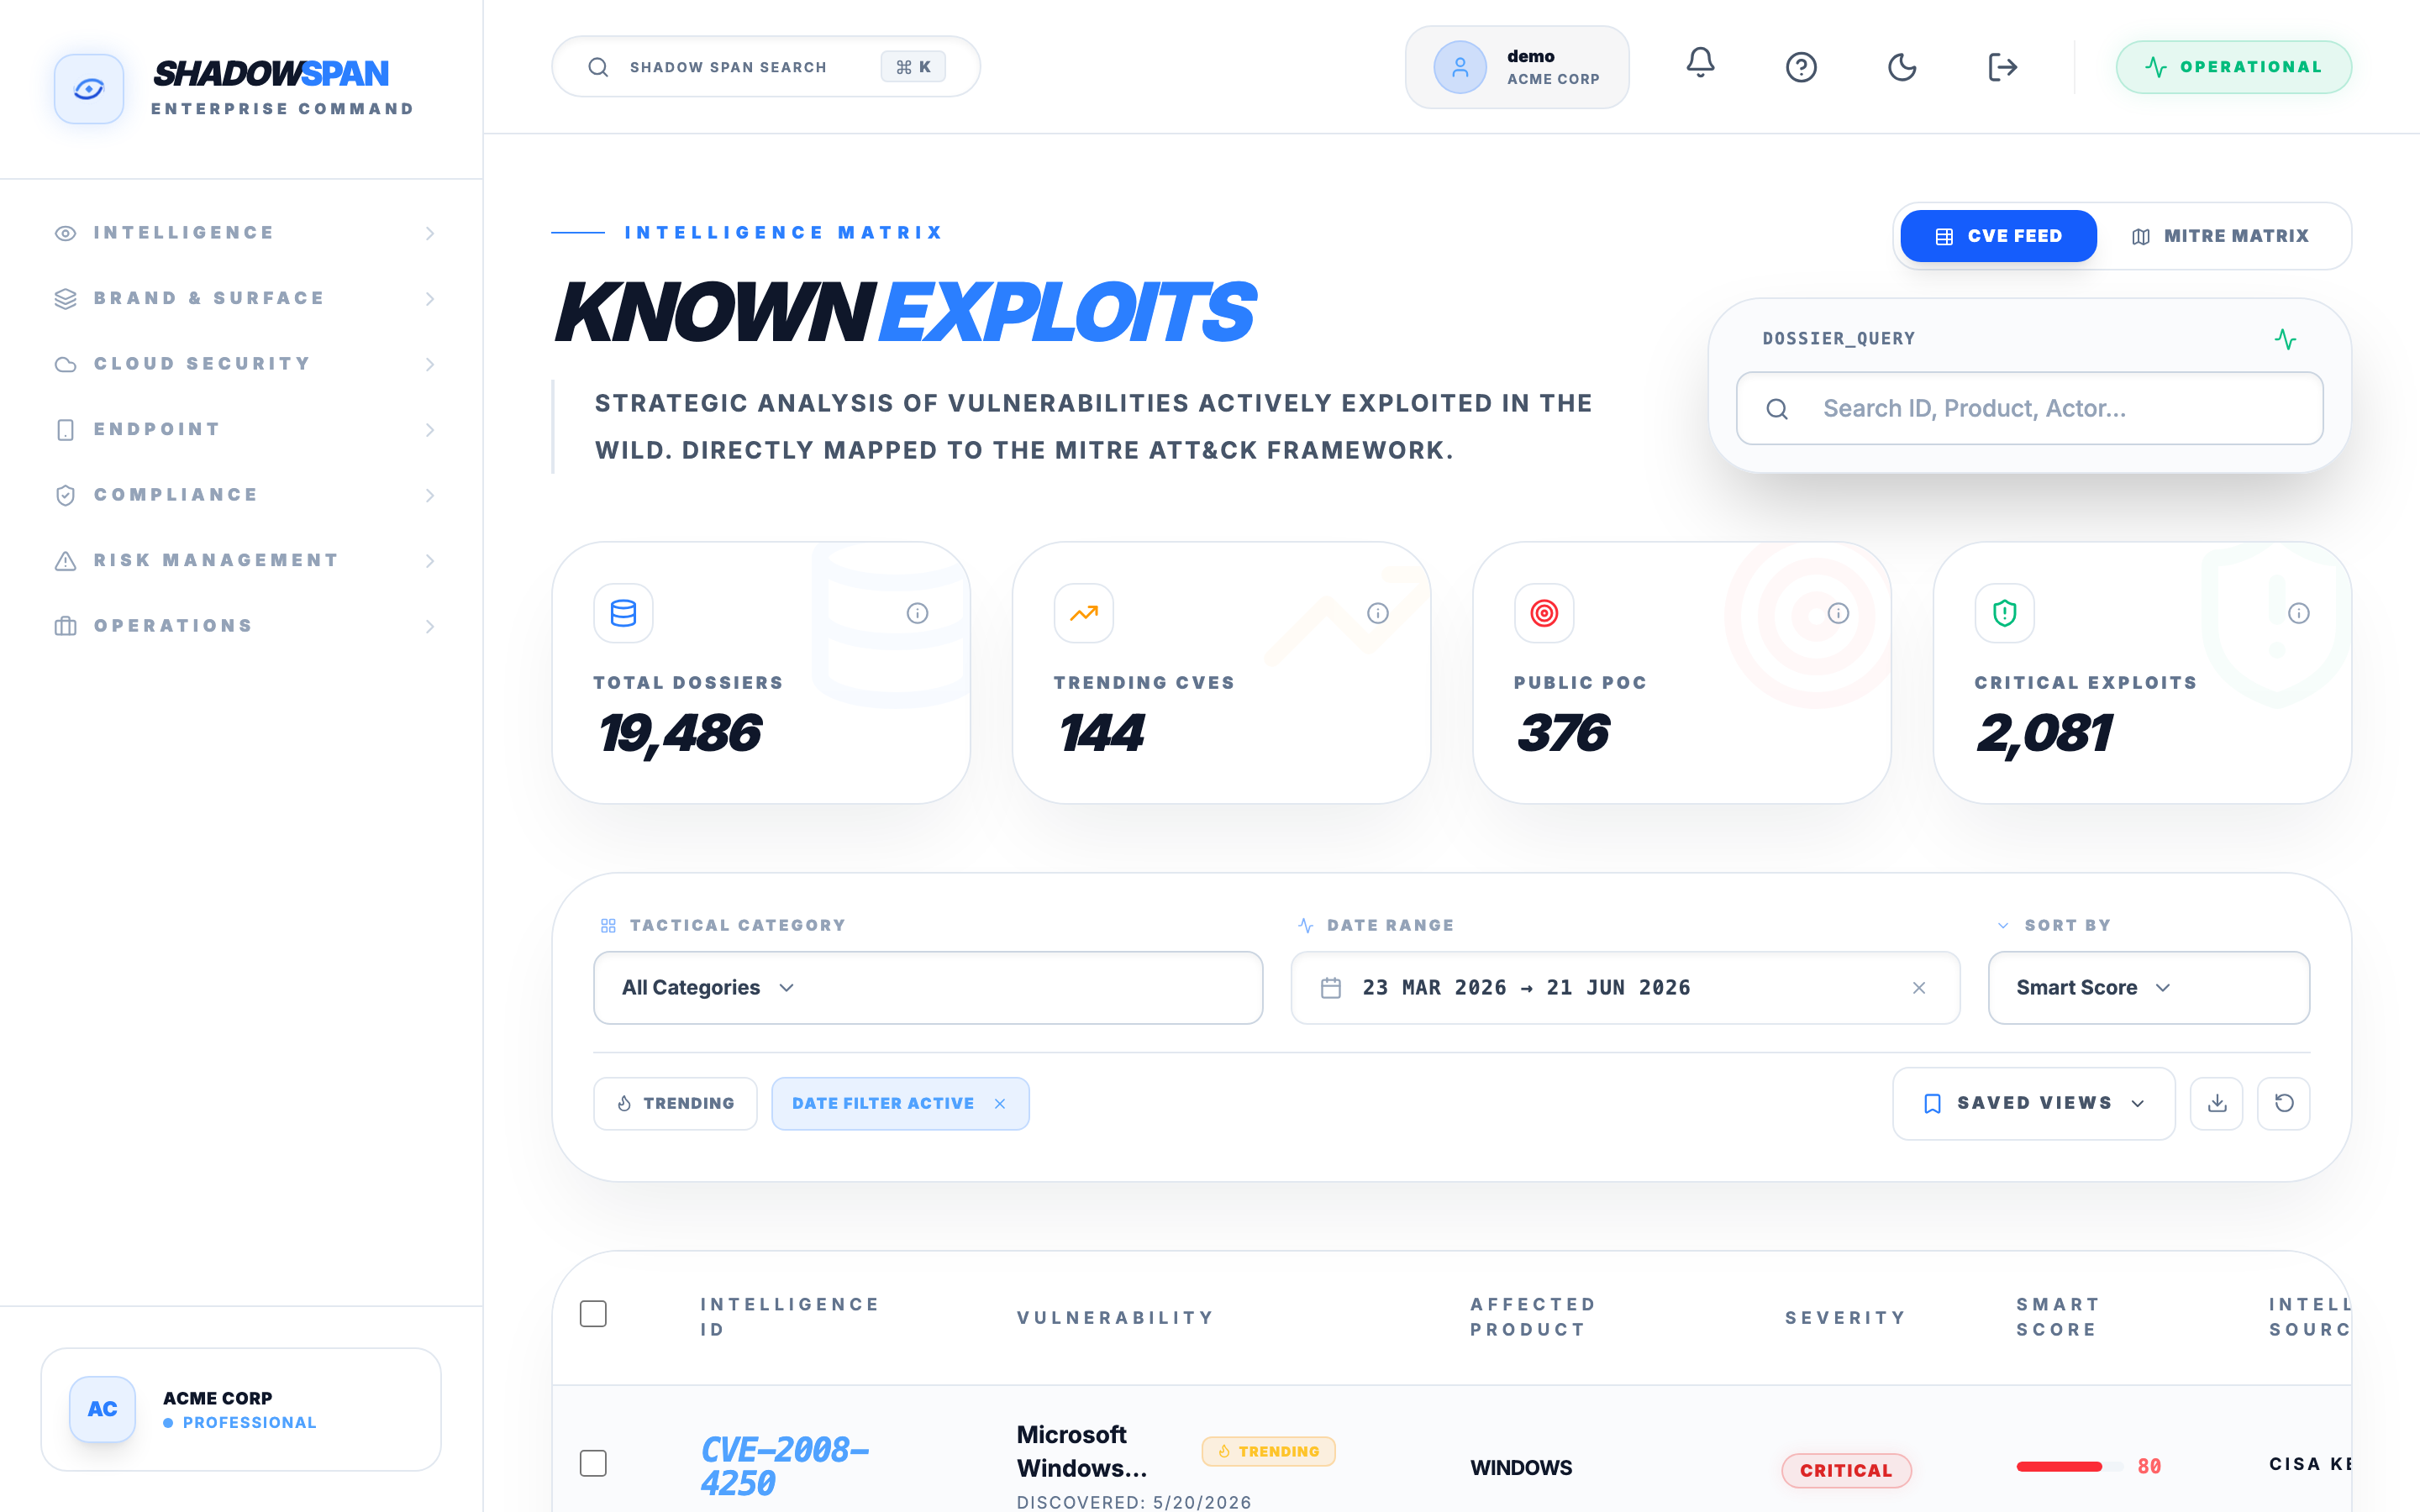
Fig. 01 — Known exploited CVEs, prioritized by Smart Score
01 · What you get
40+ aggregated sources
NVD, CISA KEV, vendor advisories, OSV, EPSS, PoC-in-GitHub, ransomware feeds and more.
Smart Score
A composite priority per CVE (up to 90) from five weighted signals.
CVE trending
Velocity scoring flags what is accelerating before it is exploited at scale.
IOC decay
Confidence ages out automatically so stale IOCs stop misleading you.
STIX / TAXII export
Feed your SIEM/SOAR through a standards-compliant server.
Natural-language query
Ask your intelligence questions in plain English.
02 · How it works
Ingest
40+ sources pulled continuously, each fault-isolated.
Dedupe + enrich
Cross-source de-duplication, EPSS and PoC enrichment.
Score + trend
Smart Score and trending velocity per CVE.
Correlate + alert
Mapped to your assets, then alerted or exported.
Most platforms resell a single feed. We own the pipeline — 40+ sources, no vendor SPOF — and correlate every CVE to your actual endpoints, cloud and exposed assets.
Works with
Replace ten tools.
One invoice.
Stop paying up to $350K a year across fragmented point solutions. Get unified visibility, cross-module correlation and AI-powered insights from a single platform.