Shadow AI · MCP governance01 / 10
AI Security
Discover every AI tool and MCP server your team installs — Claude Code, Cursor, Gemini CLI, Cline, Aider, custom MCP — without surveys. Inventory tokens at rest, flag privileged or git-tracked configs, score risk per tool. Protects what 90% of fleets can’t even see.
EASM & discovery02 / 10
External Attack Surface
5-source subdomain enumeration, port scanning, technology fingerprinting, TLS certificate monitoring, and CVE correlation for every asset you own.
40+ live sources03 / 10
Threat Intelligence
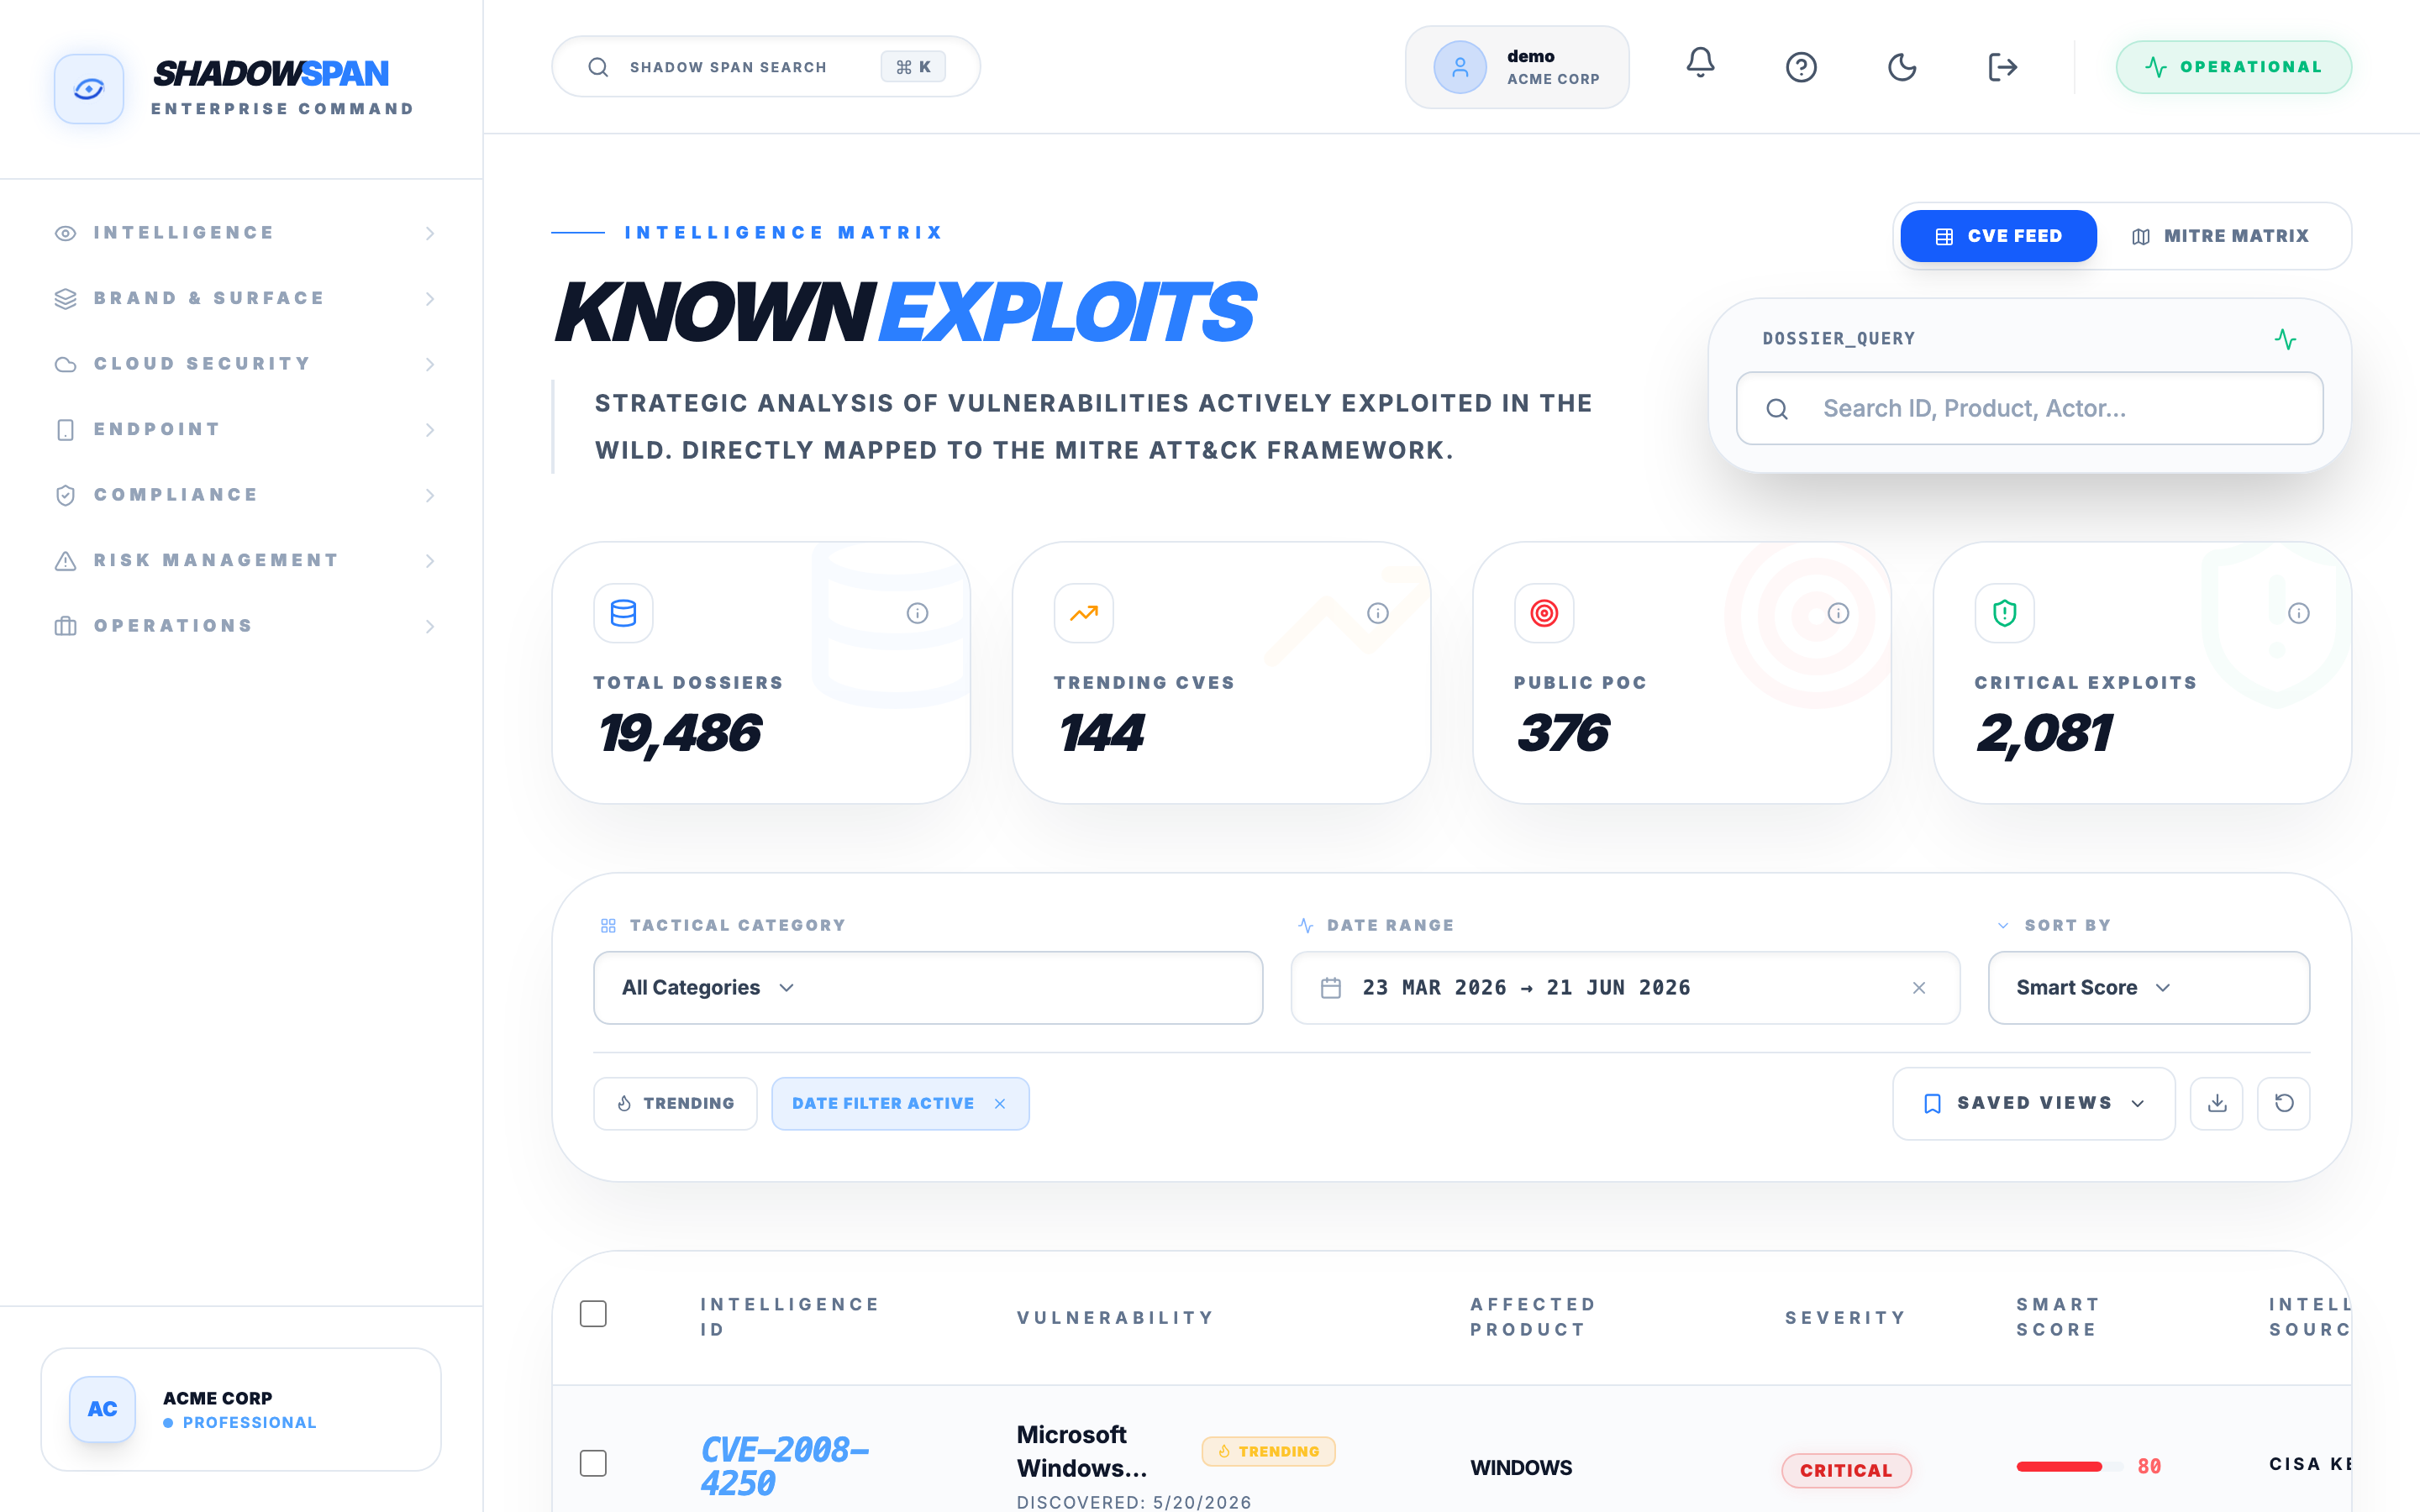
CVEs with Smart Score prioritization, EPSS exploit prediction, trending analysis, IOC tracking with confidence decay, and natural language querying.
1,000+ checks04 / 10
Cloud Security (CSPM)
Cloud security that not only looks at your configurations, but also attack path analysis, IAM gaps, and data classification to identify your most critical resources.
Detect → patch → verify05 / 10
Vulnerability Management
Endpoint agent with software inventory, automated patch jobs, maintenance windows, and post-reboot verification. Intel-driven Smart Score prioritization.
SAST · SCA · Secrets · IaC · DAST06 / 10
Application Security
Connect GitHub, GitLab, or Bitbucket and scan every repo: SAST across 9 languages, dependency CVEs, leaked secrets, IaC misconfigs, and running-app DAST — all from engines we run in-house. Call-graph reachability ranks what an attacker can actually reach first, so you fix the 30% that matters, not the noise.
Vendor intelligence07 / 10
Third-Party Risk (TPRM)
Automated questionnaires via vendor portal, AI-powered evidence analysis (SOC 2 reports, pen tests, ISO certs), residual risk scoring, and breach correlation.
Digital risk protection08 / 10
Brand & Phishing Protection
CertStream real-time detection, automated takedowns (Google Safe Browsing, Netcraft, PhishReport), app store monitoring, and social impersonation alerts.
11 frameworks + risk management09 / 10
Compliance & Risk Management
Evaluation against 11 current frameworks including the latest AI frameworks (NIST, ISO, PCI, GDPR, and regional frameworks like DORA and NIS2).
CAASM · shadow IT10 / 10
Asset Management
Cyber asset attack-surface management (CAASM): IDP integration (Okta, Azure AD, Google Workspace, OneLogin, JumpCloud) builds a unified inventory of sanctioned and unsanctioned SaaS apps with per-app user lists.