One queue for every vulnerability — patched and verified
Unify endpoint, cloud, container and internet-facing vulnerabilities into one prioritized queue — then close the loop with signed endpoint patching and post-reboot verification.
Vulnerabilities live in silos — an endpoint scanner here, a cloud tool there, an EASM list somewhere else — each with its own severity and no shared priority. And even once found, nobody closes the loop: patches get "deployed" and assumed fixed.
Shadow Span unifies vulnerabilities across endpoints, cloud workloads, containers and internet-facing assets into a single prioritized queue, ranks them by one Smart Score, tracks SLAs across all of them, and closes the loop on endpoints with signed patch jobs and post-reboot verification.
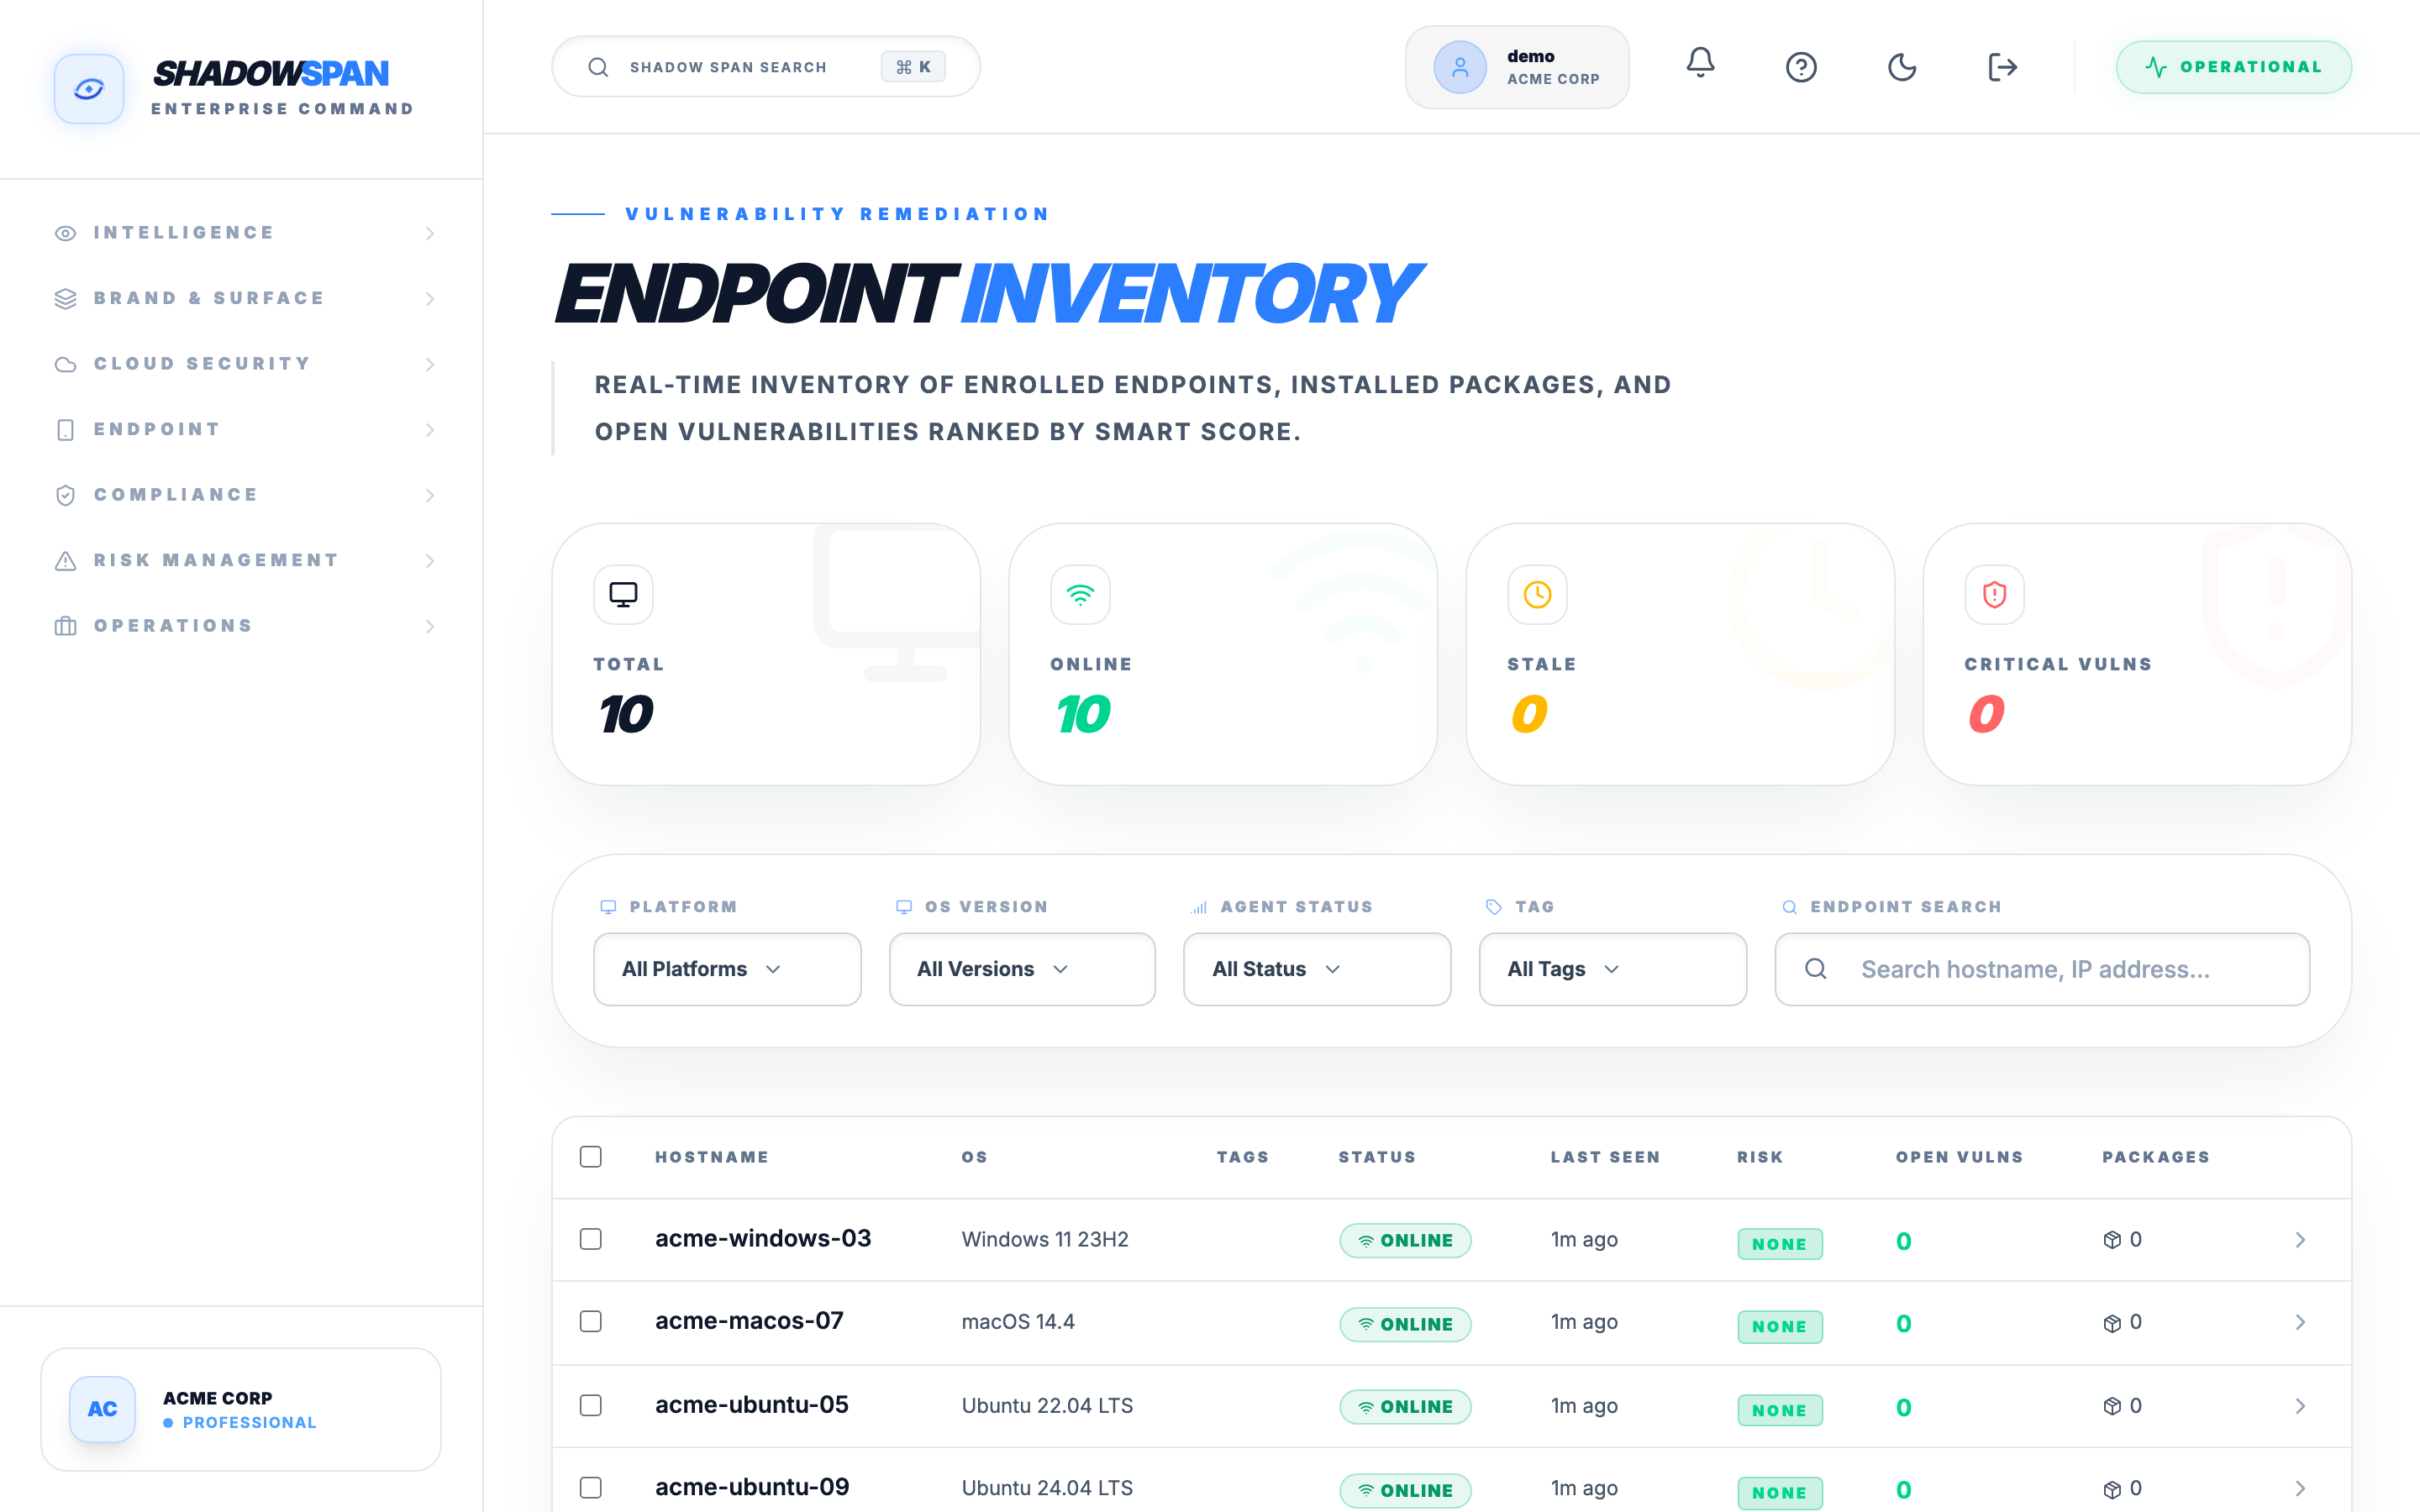
Fig. 01 — Endpoint inventory with vulnerabilities ranked by Smart Score
01 · In the product
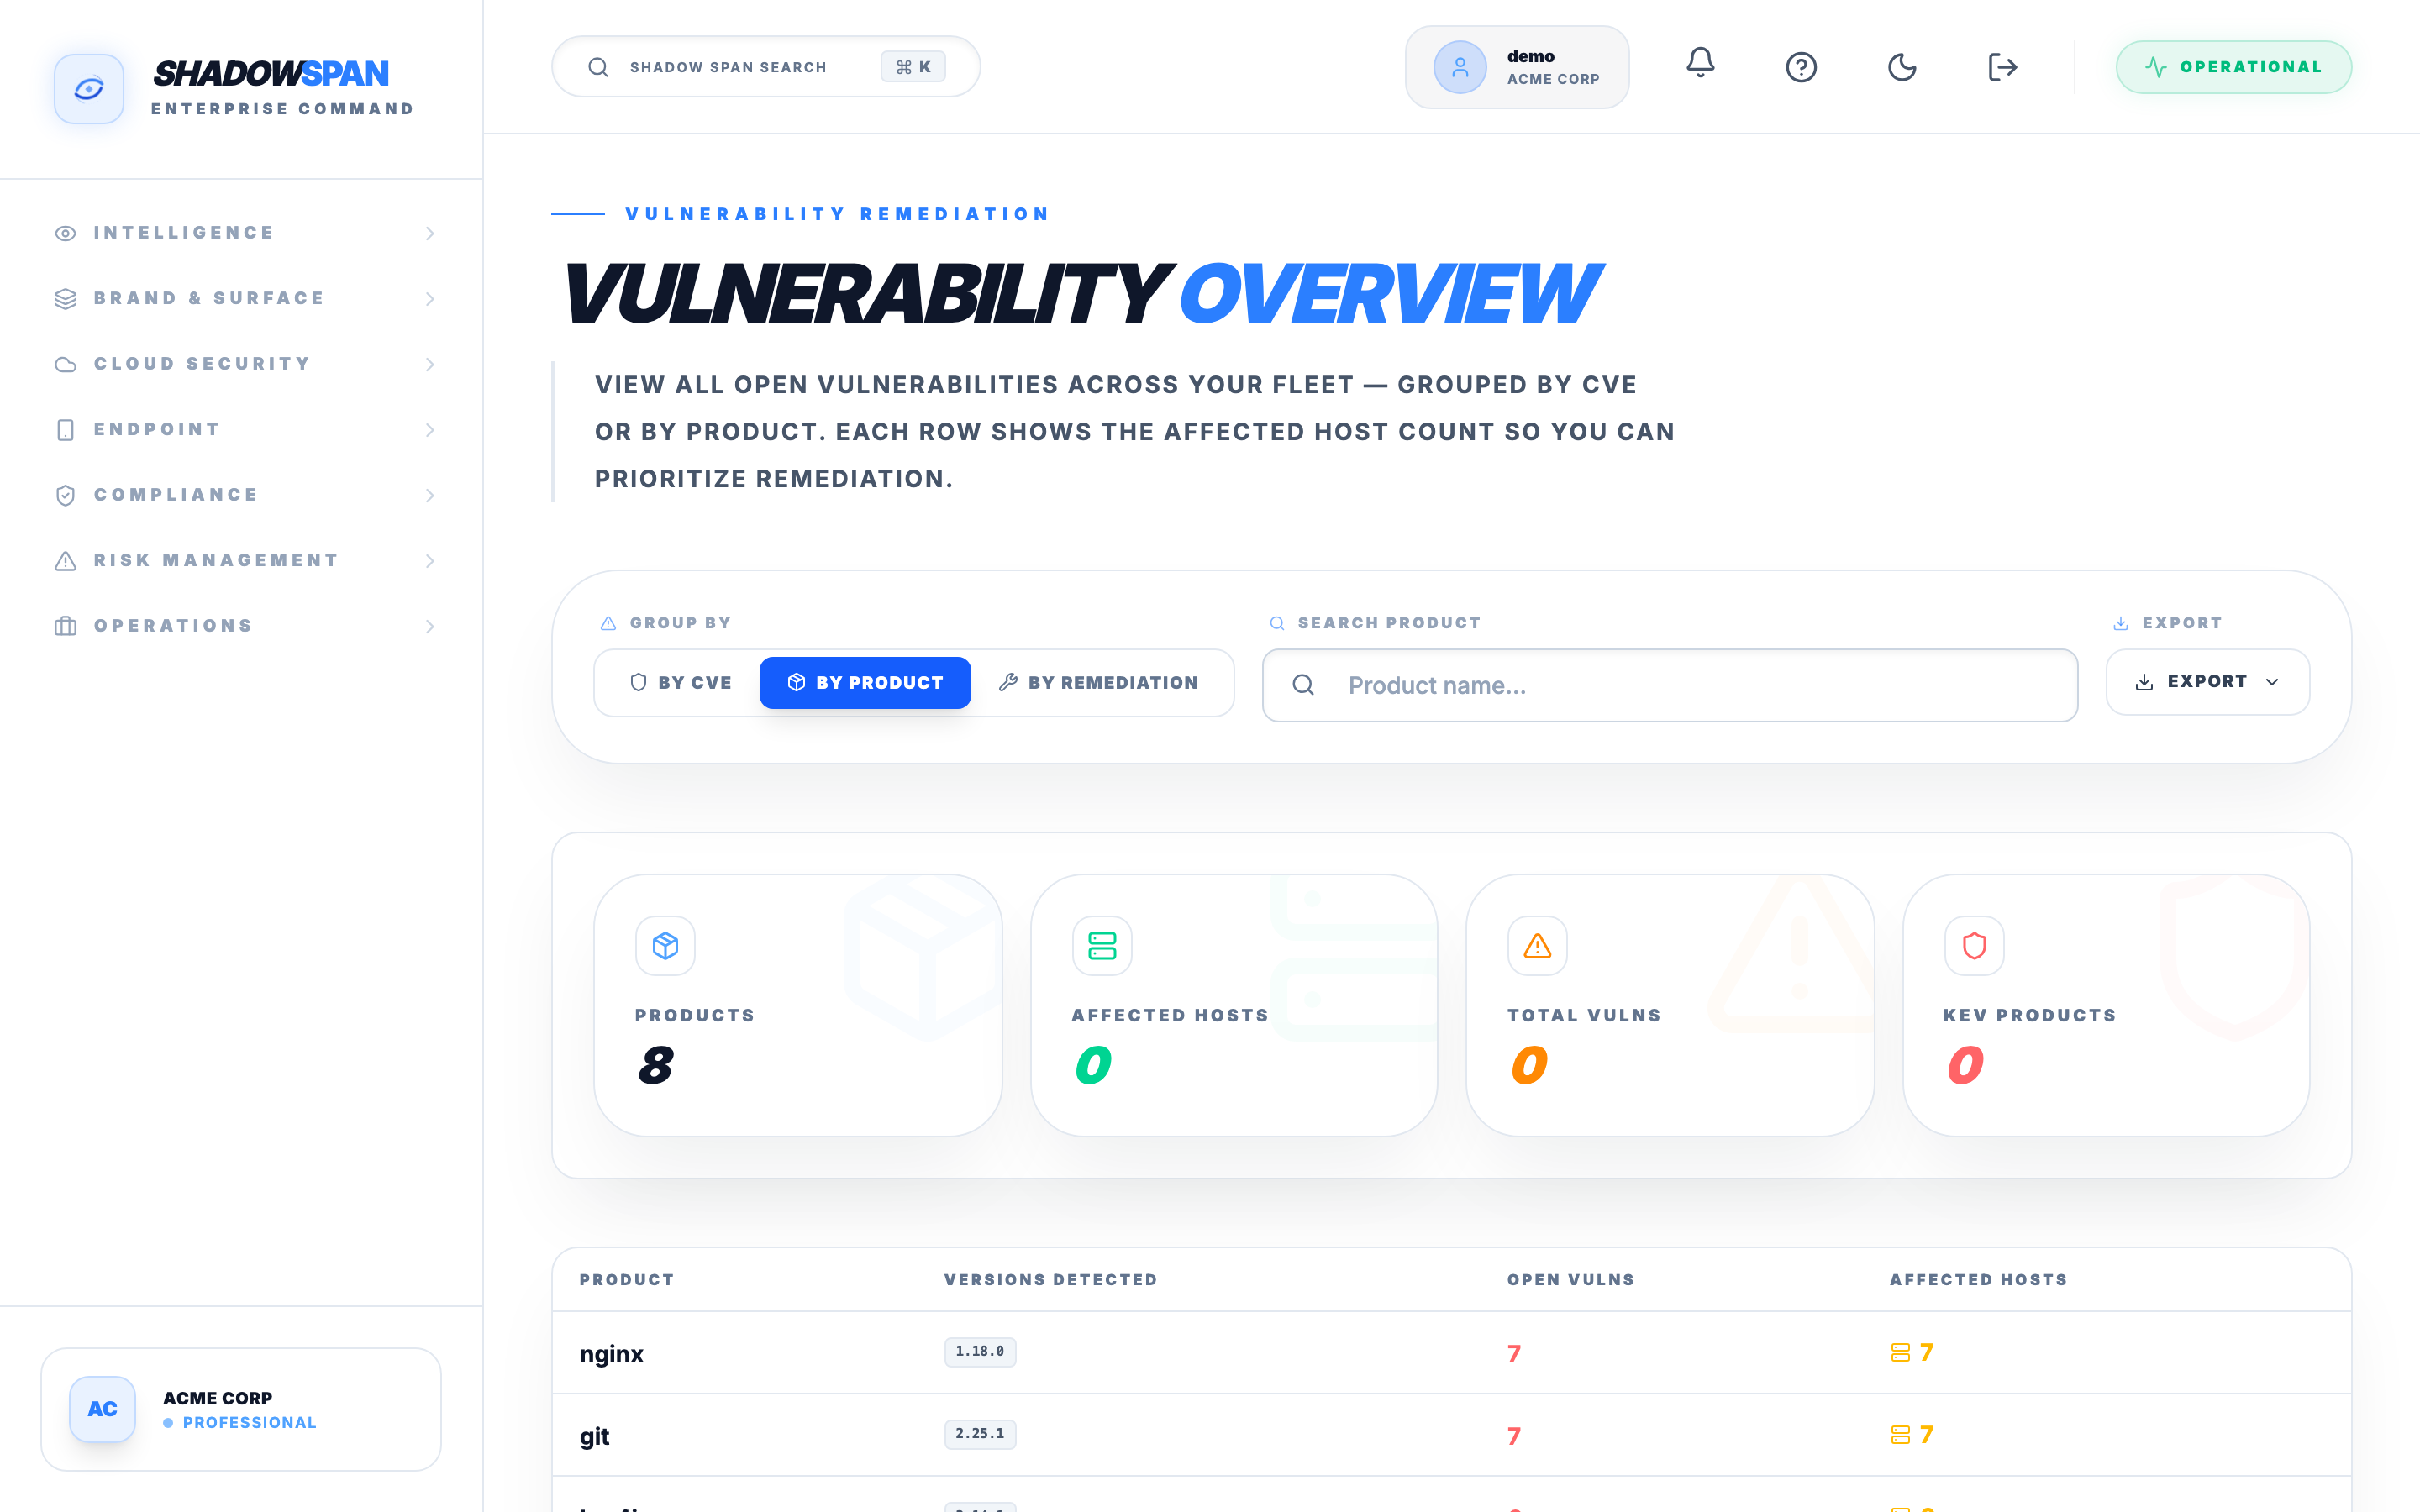
Fig. 02 — By product
Group the queue by what you patch
The same unified queue, pivoted by product — every open CVE across your fleet rolled up per software package with affected-host counts, so you fix the one upgrade that closes the most exposure instead of triaging CVEs one at a time. Group by CVE, by product, or by remediation action.
02 · What you get
One unified queue
Endpoint software, cloud-container, exposed-asset and dependency CVEs in a single prioritized view — not four siloed lists.
One Smart Score
CVSS + EPSS exploit probability + CISA KEV + public PoC + corroborating sources — the same priority across every surface.
Cross-platform agent
Linux, macOS and Windows software inventory — no surveys.
Automated endpoint patching
Signed patch commands, maintenance windows and per-OS package managers.
Post-reboot verification
Confirms the fix actually landed — not "assumed patched."
Unified SLA tracking
One deadline clock and overdue alerting across endpoint, cloud and asset vulnerabilities.
03 · How it works
Ingest from every surface
Endpoint agent, cloud/container scans and EASM correlation feed one finding model.
Prioritize once
Smart Score ranks the whole queue by real exploitable risk — across surfaces.
Patch the endpoints
Signed jobs run in maintenance windows on Linux, macOS and Windows.
Verify + track SLA
Post-reboot verification on endpoints; SLA clocks and remediation guidance on the rest.
Snyk and Aikido find the CVE and stop. Shadow Span unifies vulnerabilities from your endpoints, cloud and exposed assets into one prioritized queue — then actually patches the endpoints and proves it is gone.
Works with
Replace ten tools.
One invoice.
Stop paying up to $350K a year across fragmented point solutions. Get unified visibility, cross-module correlation and AI-powered insights from a single platform.