Cloud posture with blast radius
CSPM across GCP, AWS and Azure with attack-path analysis — not just a list of misconfigurations.
CSPM tools dump thousands of misconfigs with no context, so you cannot tell a public test bucket from a path to your crown jewels.
1,000+ checks across three clouds, plus IAM-graph analysis, toxic-combination detection and attack-path inference that shows how a misconfig chains to a privileged role or sensitive data.
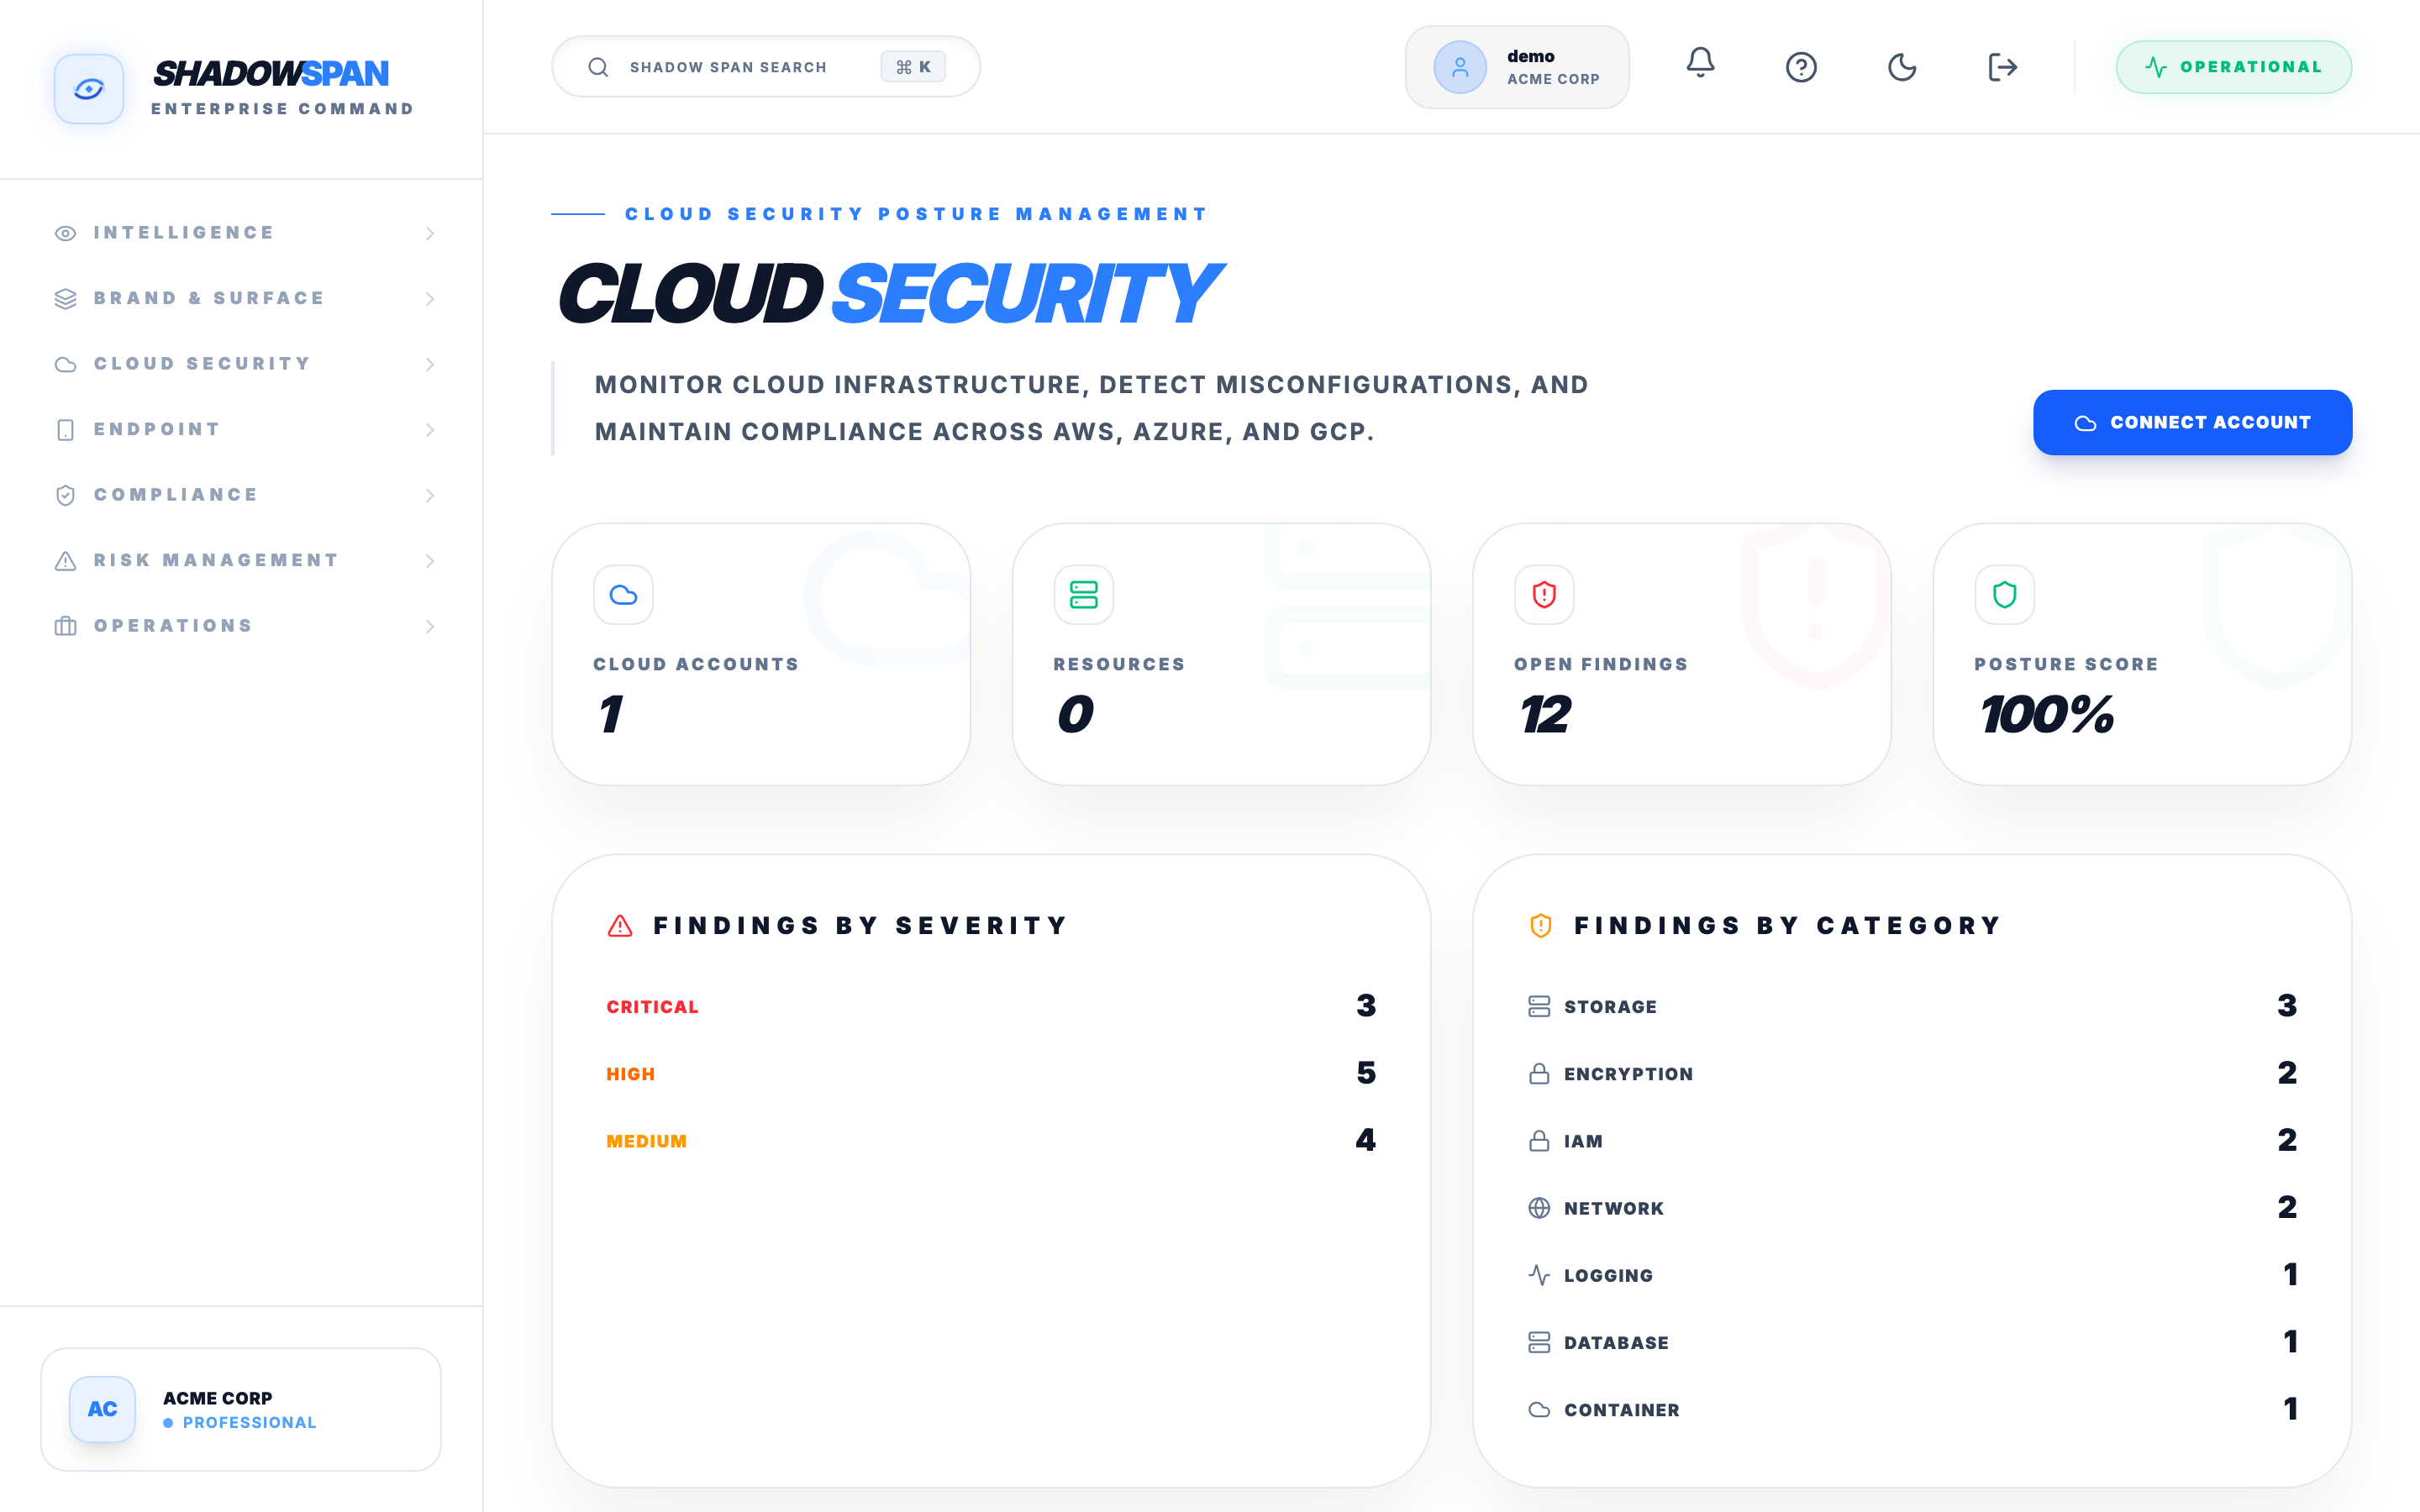
Fig. 01 — Misconfigurations by severity and category across your cloud
01 · What you get
1,000+ posture checks
GCP, AWS and Azure, evaluated continuously against industry hardening baselines and framework controls.
IAM graph
Who can reach what — including INVOKES / AUTHENTICATES privilege-escalation edges.
Attack paths
Toxic combinations chained from public exposure → workload → privileged role.
Container scanning
Trivy image scanning on every pushed digest, grouped by repo.
Coverage-gap telemetry
Surfaces resource types not yet covered so nothing is silently missed.
Compliance mapping
Every check maps to SOC 2 / ISO / PCI / NIST controls.
02 · How it works
Grant read-only access
A scoped role per cloud — no agents, no write access.
Inventory + checks
Continuous resource inventory and 1,000+ posture evaluations.
Graph + attack paths
IAM graph and toxic-combo inference compute real blast radius.
Prioritized + mapped
Findings ranked by exploitability and mapped to your frameworks.
Wiz-style attack paths, unified with your AppSec, EASM and endpoint findings in one graph — and priced for teams that are not a Fortune 500.
Works with
Replace ten tools.
One invoice.
Stop paying up to $350K a year across fragmented point solutions. Get unified visibility, cross-module correlation and AI-powered insights from a single platform.