Govern the AI your team already runs
Discover every AI tool and MCP server on your fleet — without sending a single survey.
Developers adopt AI coding tools and MCP servers faster than security can track. Most fleets cannot even see what is installed, let alone what tokens it holds.
The endpoint agent discovers every AI CLI and MCP server, inventories tokens at rest, flags privileged / no-auth / git-tracked configs, scores per-tool risk, and scans transcripts for leaked secrets — all on-device.
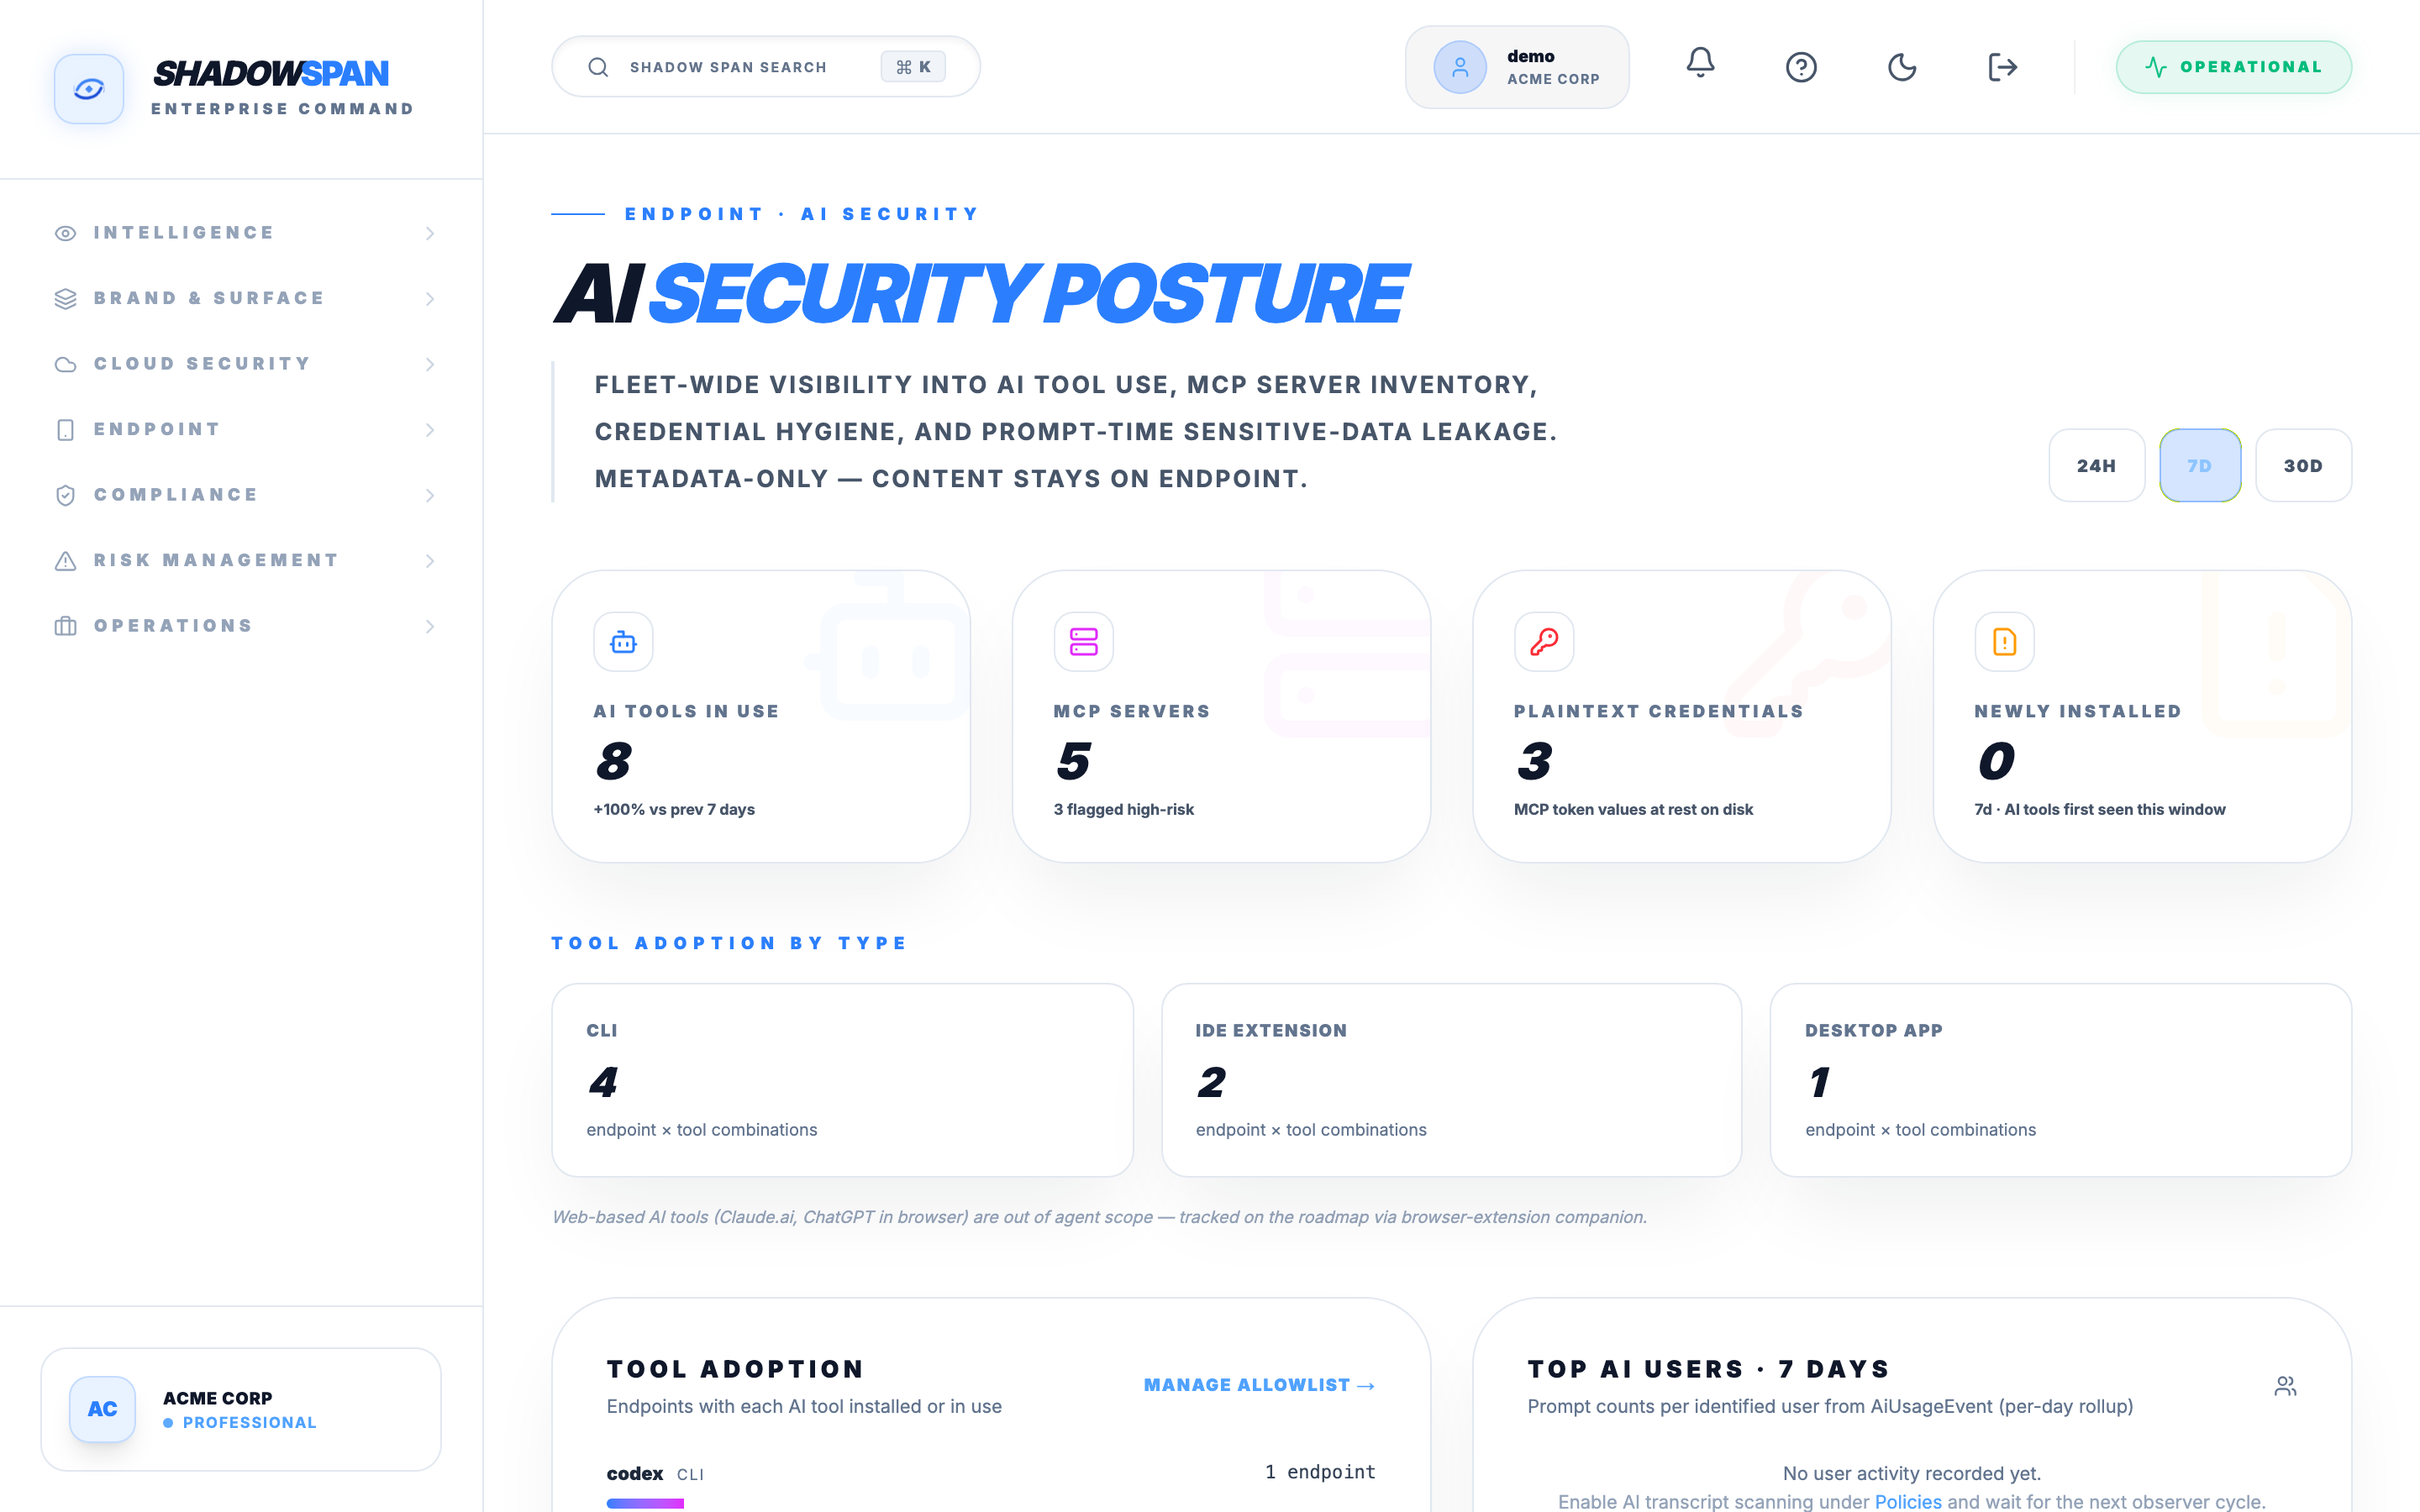
Fig. 01 — Fleet-wide AI tool + MCP server inventory and risk
01 · What you get
AI tool inventory
Every CLI agent (Claude Code, Cursor, Gemini CLI, Cline, Aider, custom MCP) per endpoint + user.
MCP server governance
Risk scored by auth model × privilege × token blast-radius × provenance.
Secret-in-config detection
Plaintext tokens, git-tracked configs and remote-no-HTTPS servers.
Transcript DLP
On-device scanning for leaked credentials; content never leaves the endpoint.
Policy + alerting
Live rules, auto-Case on critical, and approved-tool allowlists.
Consent-gated
Per-org opt-in, evidence-level ceilings and user pseudonymization.
02 · How it works
Deploy the agent
The same Aegis agent, with AI observers consent-gated on.
Observe on-device
Configs and transcripts are inspected locally, never uploaded.
Risk-score
Per-tool and per-MCP risk from auth, privilege and provenance.
Govern
Policy rules raise alerts and open Cases on critical findings.
The AI-governance category Snyk and Aikido do not have at all — a first-class module, not a checkbox, and tied to your compliance AI frameworks.
Works with
Replace ten tools.
One invoice.
Stop paying up to $350K a year across fragmented point solutions. Get unified visibility, cross-module correlation and AI-powered insights from a single platform.